Will Seligman
Cybersecurity Operations | Threat Hunting | Threat Intelligence | Detection Engineering | Incident Response | Incident Commander | Automation Implementation
LinkedIn ↗ Twitter ↗ Discord ↗ GitHub ↗
Research
Cross-Platform Rust Loader Delivers Modified Sliver Implant via Cloud Storage Abuse
Novel threat uncovered: RADICL identifies a previously unseen cross-platform Rust loader delivering a modified Sliver C2 fork via cloud storage abuse. Full IOCs & YARA inside.
 radicl.com/resources/cross-platform-rust-loader-delivers-modified-sliver-implant-via-cloud-storage-abuse
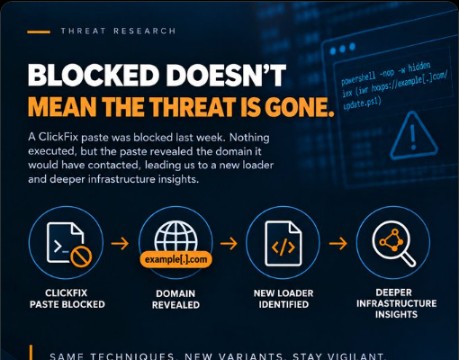
Blocked ClickFix Paste Leads to Low-Detection Loader Tied to KongTuke/TAG-124
A blocked ClickFix paste's leftover domain led RADICL to a C-based loader flagged by just 2 of 76 VirusTotal engines, sharing core design with malware previously analyzed by Unit42. Delivery infrastructure overlaps with KongTuke/TAG-124 across five samples and two build dates.
Repositories
malware-research
github.com/the-grizzly-bear/malware-research
threat-research
github.com/the-grizzly-bear/threat-research
threat-emulation
github.com/the-grizzly-bear/threat-emulation
yara-rules
github.com/the-grizzly-bear/yara-rules
sigma-rules
github.com/the-grizzly-bear/sigma-rules
cve-exploits
github.com/the-grizzly-bear/cve-exploits
mcp-server
github.com/the-grizzly-bear/mcp-server
cti-engine
github.com/the-grizzly-bear/cti-engine
agent-dashboard
github.com/the-grizzly-bear/agent-dashboard