5
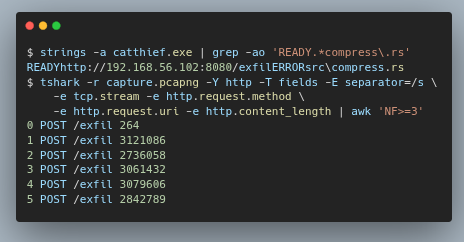
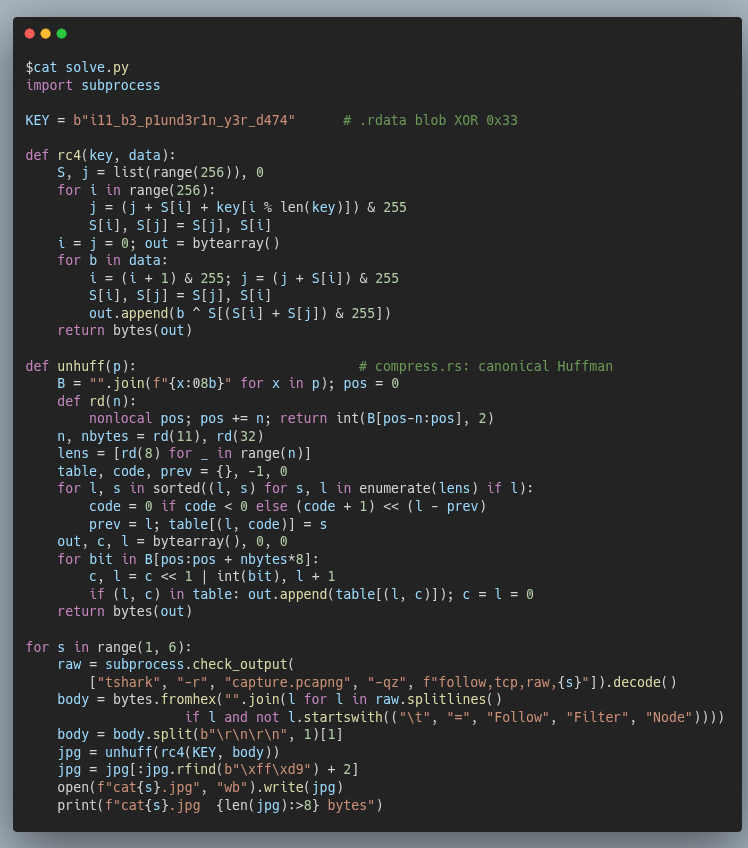
Rust exe + pcap. Client POSTs to /exfil, the server replies with a file path, and the client sends that file back
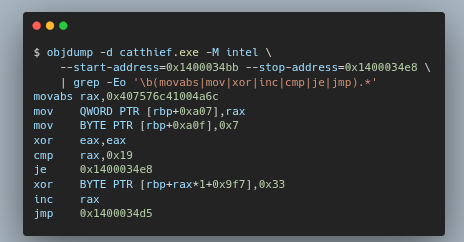
The exe embeds an RC4 key in .rdata, obfuscated with XOR 0x33
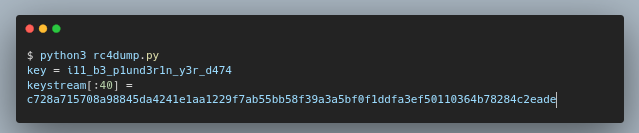
De-obfuscating it gives the key i11_b3_p1und3r1n_y3r_d474, whose keystream matches the pcap
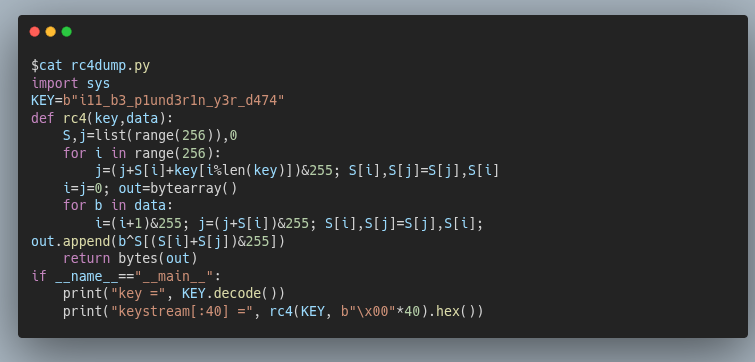
RC4-decrypting each server response reveals the file it asked the client to steal
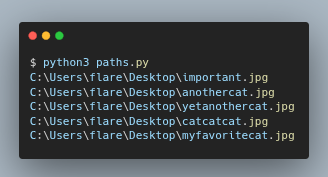
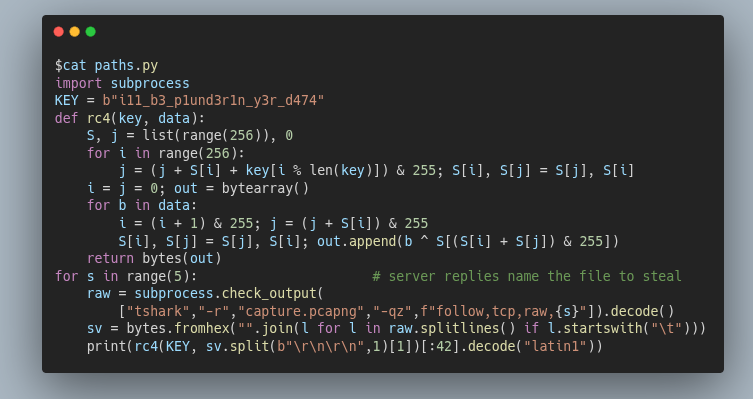
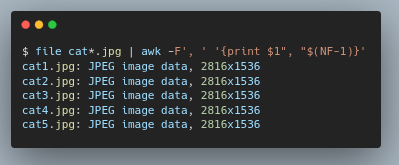
The uploaded bodies are RC4-encrypted then Huffman-compressed (compress.rs). Undo both to recover 5 JPEGs
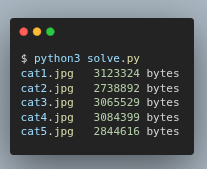
myfavoritecat.jpg
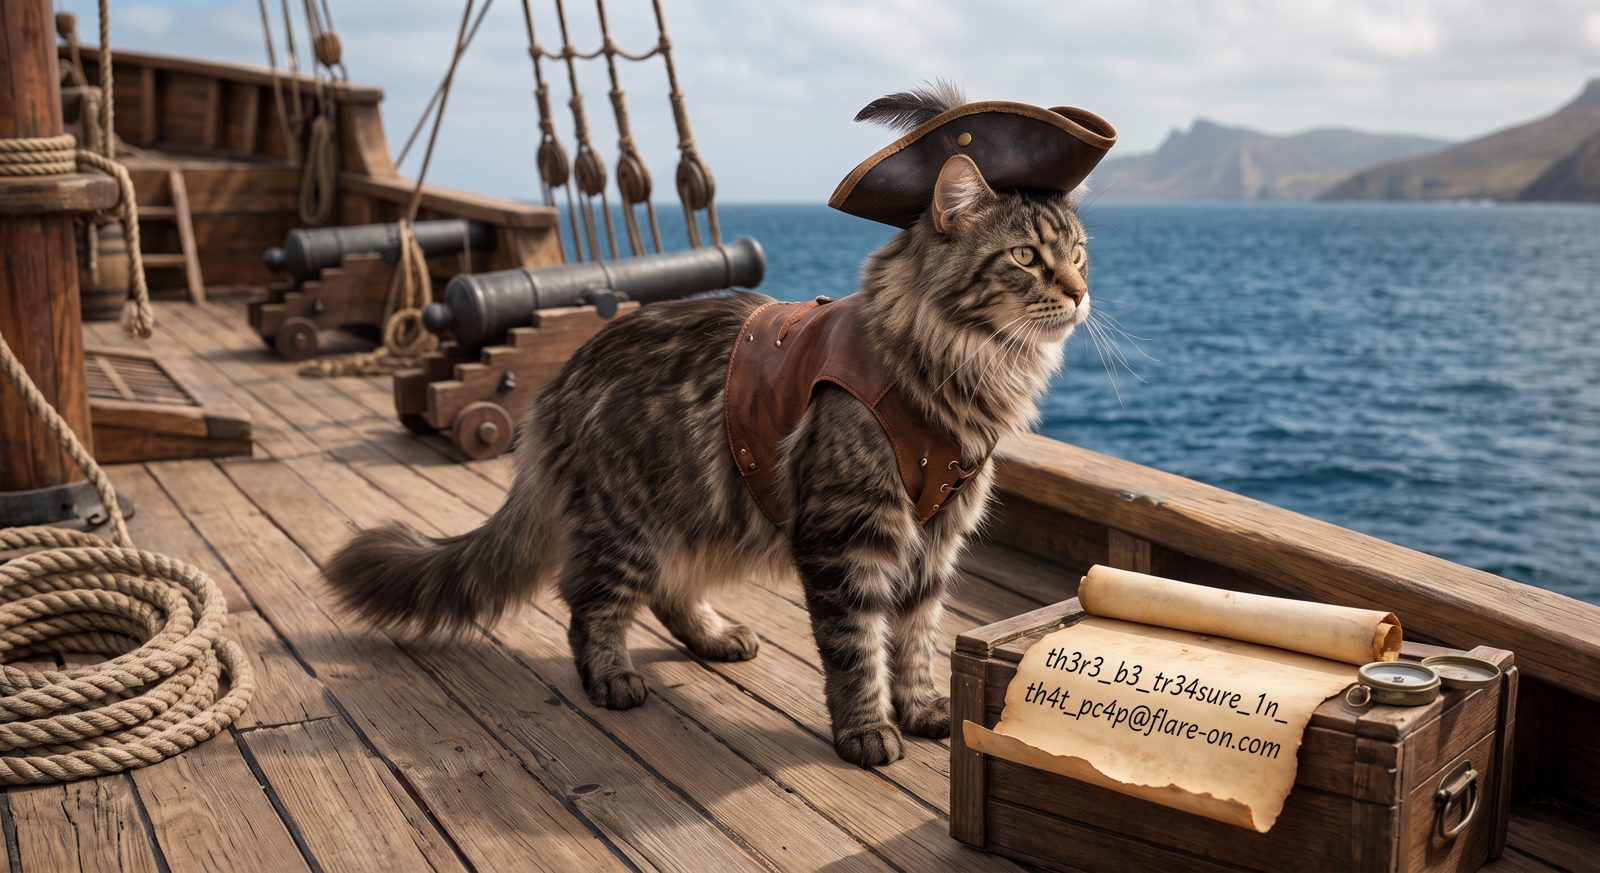
th3r3_b3_tr34sure_1n_th4t_pc4p@flare-on.com