2024-10-12 X-RAY (Malware)
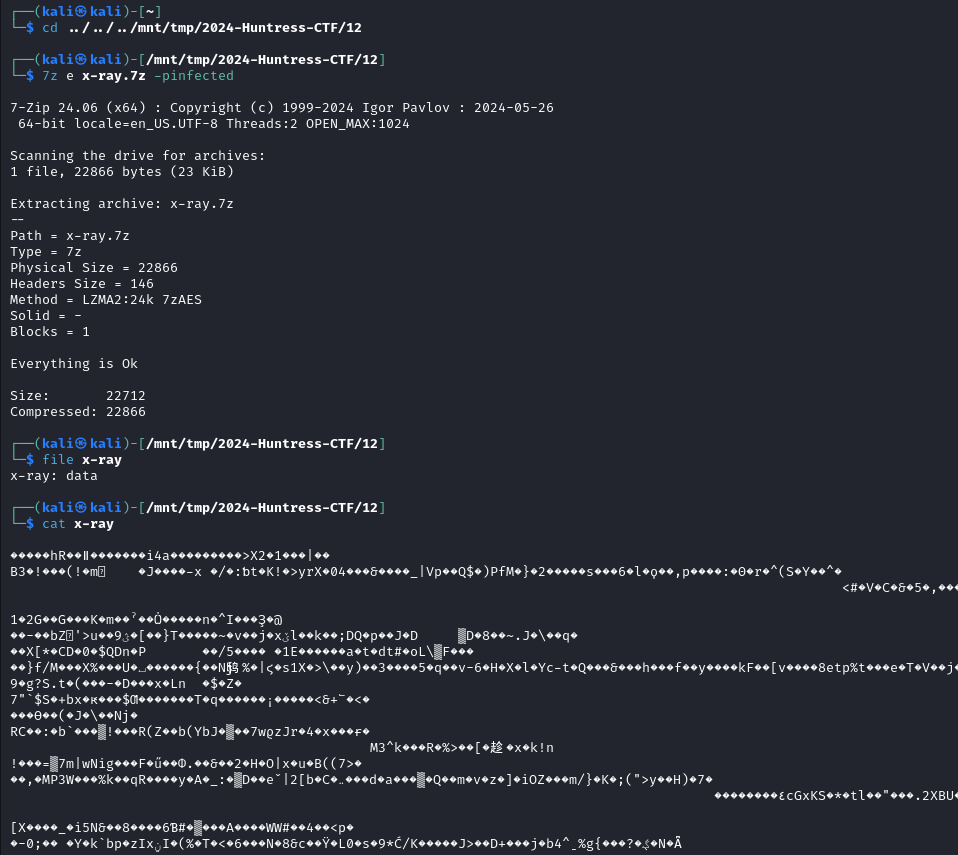
https://hexacorn.com/d/DeXRAY.pl
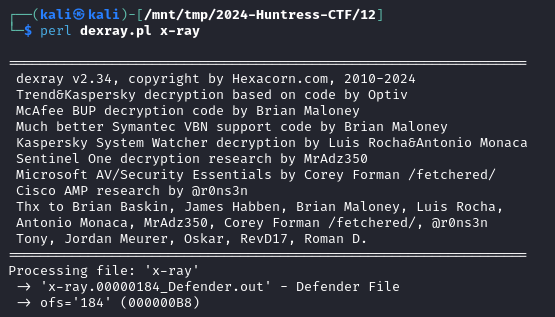
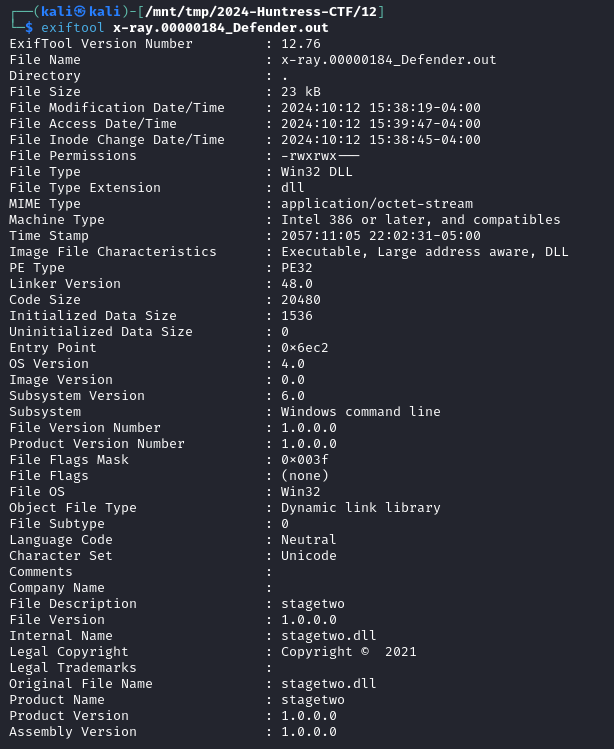
First time around it should have opened up in dnspy, but I was extracting from defender, rather than just using dexray to dump then view the file.
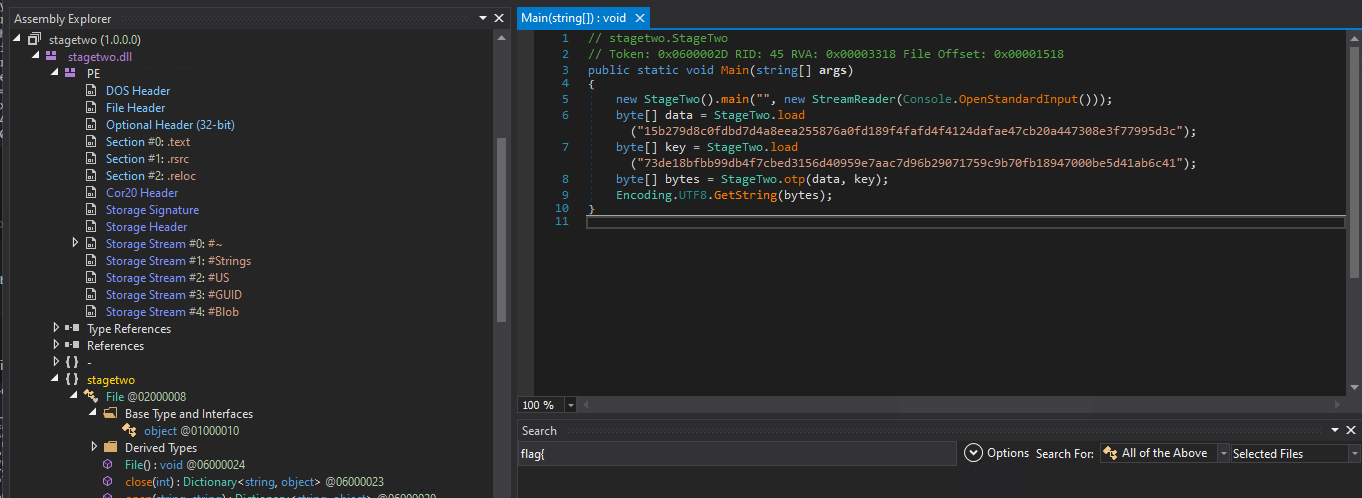
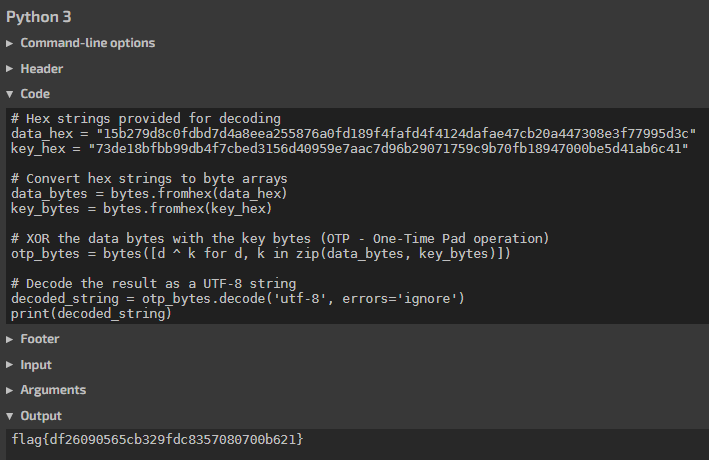
flag{df26090565cb329fdc8357080700b621}# Hex strings provided for decoding
data_hex = "15b279d8c0fdbd7d4a8eea255876a0fd189f4fafd4f4124dafae47cb20a447308e3f77995d3c"
key_hex = "73de18bfbb99db4f7cbed3156d40959e7aac7d96b29071759c9b70fb18947000be5d41ab6c41"
# Convert hex strings to byte arrays
data_bytes = bytes.fromhex(data_hex)
key_bytes = bytes.fromhex(key_hex)
# XOR the data bytes with the key bytes (OTP - One-Time Pad operation)
otp_bytes = bytes([d ^ k for d, k in zip(data_bytes, key_bytes)])
# Decode the result as a UTF-8 string
decoded_string = otp_bytes.decode('utf-8', errors='ignore')
decoded_stringRabbit hole
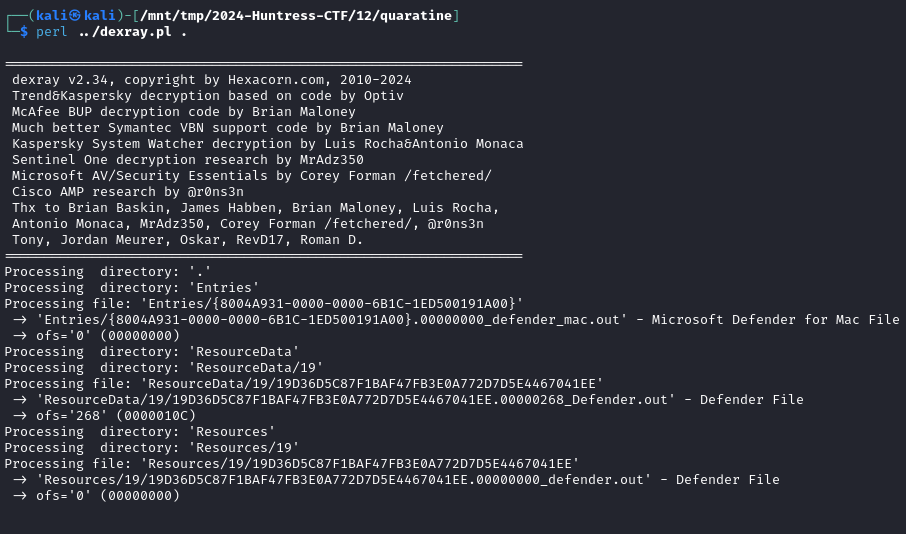
I first tired to extract the quarantined file from defender, then copy, and run again, was giving me errors.
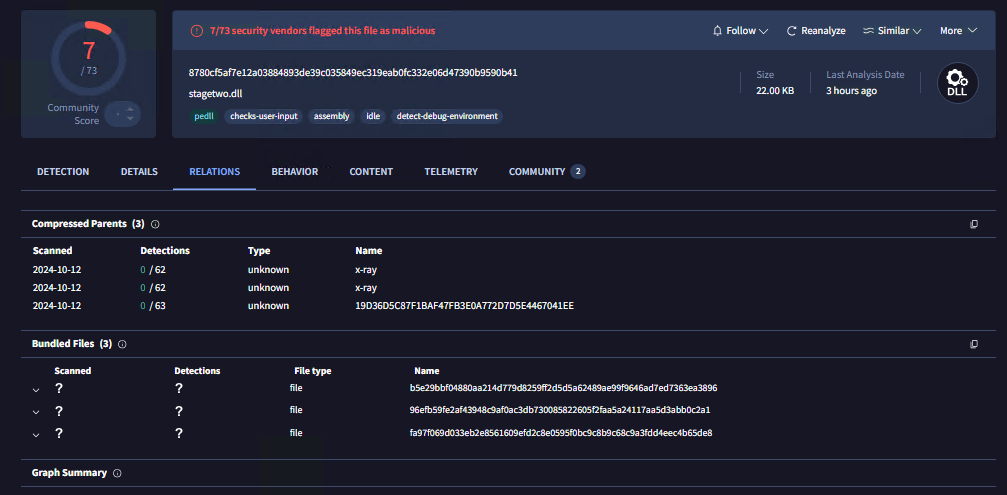
VirusTotal
VirusTotal
https://www.virustotal.com/gui/file/8780cf5af7e12a03884893de39c035849ec319eab0fc332e06d47390b9590b41/behavior
Analog | Triage™
https://tria.ge/241012-yt1tcatbll/behavioral1/analog?q=&offset=4
https://www.youtube.com/watch?v=K60kriw4o44