All the Links

Government resources

CISA Cybersecurity Advisories
https://www.cisa.gov/uscert/ncas/alerts.xml
Alerts
https://www.cisa.gov/uscert/ncas/current-activity.xml
CISA Analysis Reports
https://www.cisa.gov/uscert/ncas/analysis-reports.xml
Bulletins
https://www.cisa.gov/uscert/ncas/bulletins.xml

Malware

VirusTotal
VirusTotal
https://www.virustotal.com/gui/home/upload
MalwareBazaar | Malware sample exchange
MalwareBazaar is a project of abuse.ch with the goal of sharing malware samples
https://bazaar.abuse.ch/
capa Explorer Web
https://mandiant.github.io/capa/explorer/#/
Malpedia (Fraunhofer FKIE)
Malpedia is a free service offered by Fraunhofer FKIE. Administration is lead by Daniel Plohmann and Steffen Enders.
https://malpedia.caad.fkie.fraunhofer.de/

REversing
Decompiler Explorer
Decompiler Explorer is an interactive online decompiler which shows equivalent C-like output of decompiled programs from many popular decompilers.
https://dogbolt.org/
Compiler Explorer
Compiler Explorer is an interactive online compiler which shows the assembly output of compiled C++, Rust, Go (and many more) code.
https://godbolt.org/
GitHub - dnSpy/dnSpy: .NET debugger and assembly editor
.NET debugger and assembly editor. Contribute to dnSpy/dnSpy development by creating an account on GitHub.
https://github.com/dnSpy/dnSpy

https://autogdb.io/

Malware Analysis

Binary Ninja Cloud
Binary Ninja Cloud is a completely free, online, collaborative reverse engineering suite, which uses Binary Ninja for analysis.
https://cloud.binary.ninja/
GitHub - ReFirmLabs/binwalk: Firmware Analysis Tool
Firmware Analysis Tool. Contribute to ReFirmLabs/binwalk development by creating an account on GitHub.
https://github.com/ReFirmLabs/binwalk
GitHub - e-m-b-a/emba: EMBA - The firmware security analyzer
EMBA - The firmware security analyzer. Contribute to e-m-b-a/emba development by creating an account on GitHub.
https://github.com/e-m-b-a/emba
GitHub - onekey-sec/unblob: Extract files from any kind of container formats
Extract files from any kind of container formats. Contribute to onekey-sec/unblob development by creating an account on GitHub.
https://github.com/onekey-sec/unblob
GitHub - redballoonsecurity/ofrak: OFRAK: unpack, modify, and repack binaries.
OFRAK: unpack, modify, and repack binaries. Contribute to redballoonsecurity/ofrak development by creating an account on GitHub.
https://github.com/redballoonsecurity/ofrak

https://github.com/avatortwo/avatar2
GitHub - radareorg/radare2: UNIX-like reverse engineering framework and command-line toolset
UNIX-like reverse engineering framework and command-line toolset - radareorg/radare2
https://github.com/radareorg/radare2
GitHub - renode/renode: Renode - Antmicro's open source simulation and virtual development framework for complex embedded systems
Renode - Antmicro's open source simulation and virtual development framework for complex embedded systems - renode/renode
https://github.com/renode/renode
GitHub - panda-re/panda: Platform for Architecture-Neutral Dynamic Analysis
Platform for Architecture-Neutral Dynamic Analysis - panda-re/panda
https://github.com/panda-re/panda
GitHub - hasherezade/pe-bear-old: PE-bear (builds only)
PE-bear (builds only). Contribute to hasherezade/pe-bear-old development by creating an account on GitHub.
https://github.com/hasherezade/pe-bear-releases
Internet Archive: Digital Library of Free & Borrowable Texts, Movies, Music & Wayback Machine
https://archive.org/details/malwaremuseum
GitHub - Karneades/awesome-malware-persistence: A curated list of awesome malware persistence tools and resources.
A curated list of awesome malware persistence tools and resources. - Karneades/awesome-malware-persistence
https://github.com/Karneades/awesome-malware-persistence
VX Vault
http://vxvault.net/ViriList.php
Reports | Triage™
https://tria.ge/reports/public
GitHub - katahiromz/RisohEditor: Another free Win32 resource editor
Another free Win32 resource editor. Contribute to katahiromz/RisohEditor development by creating an account on GitHub.
https://github.com/katahiromz/RisohEditor
Build software better, together
GitHub is where people build software. More than 150 million people use GitHub to discover, fork, and contribute to over 420 million projects.
https://github.com/topics/scgdb-data
GitHub - JPCERTCC/YAMA: Yet Another Memory Analyzer for malware detection
Yet Another Memory Analyzer for malware detection. Contribute to JPCERTCC/YAMA development by creating an account on GitHub.
https://github.com/JPCERTCC/YAMA
binvis.io
https://binvis.io/

Malware tracking

C2 Panel Tracker — ViriBack C2 Tracker
https://tracker.viriback.com/

Forensics and DFIR

GitHub - volatilityfoundation/volatility3: Volatility 3.0 development
Volatility 3.0 development. Contribute to volatilityfoundation/volatility3 development by creating an account on GitHub.
https://github.com/volatilityfoundation/volatility3
sigma/rules-dfir at master · SigmaHQ/sigma
Main Sigma Rule Repository. Contribute to SigmaHQ/sigma development by creating an account on GitHub.
https://github.com/SigmaHQ/sigma/tree/master/rules-dfir
The DFIR Report
The DFIR Report has 9 repositories available. Follow their code on GitHub.
https://github.com/The-DFIR-Report
Intelligence Portals - AboutDFIR - The Definitive Compendium Project
https://aboutdfir.com/research/intelligence-portals/

MITRE

https://mitre-attack.github.io/attack-navigator/
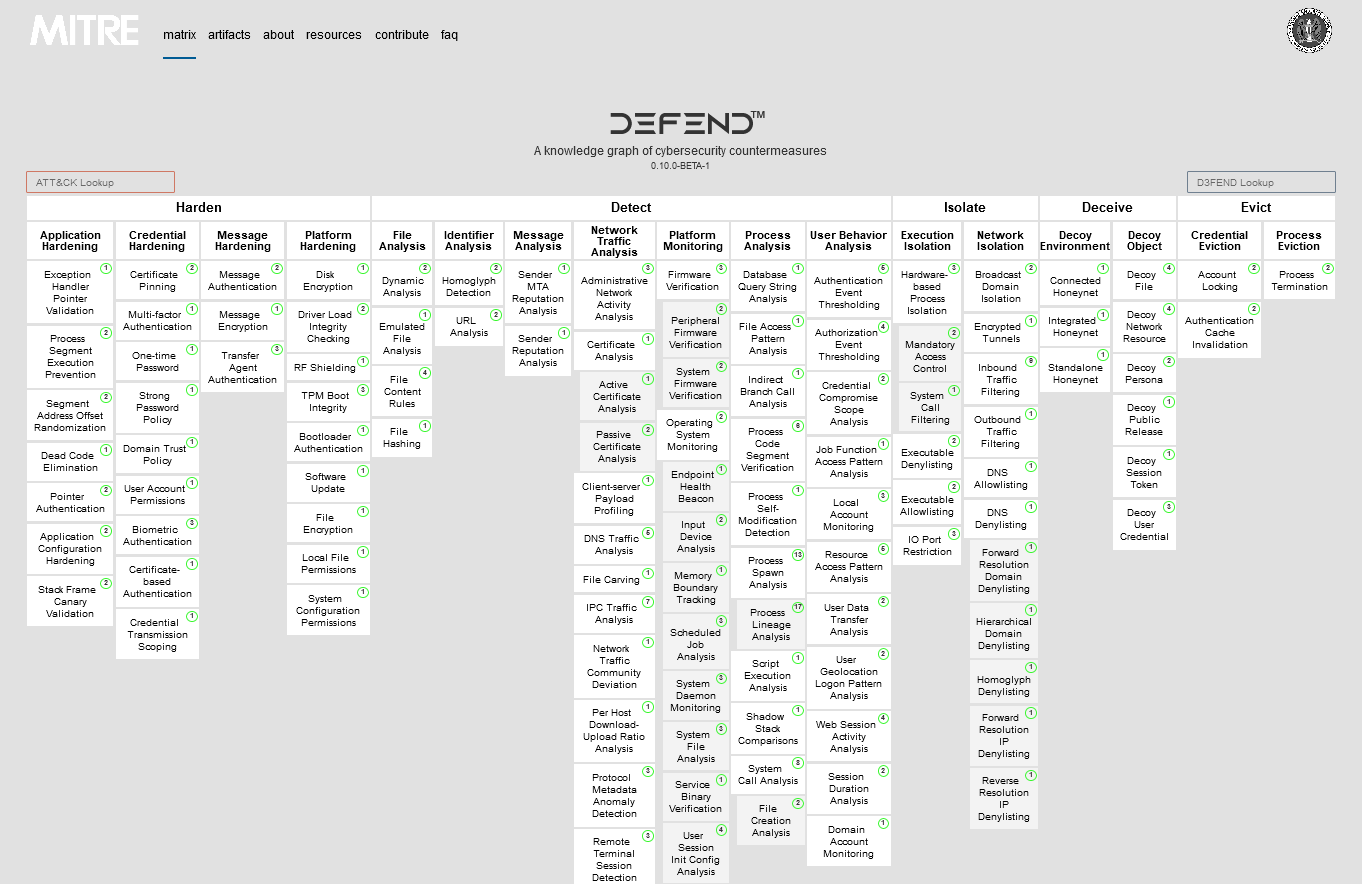
MITRE D3FEND Knowledge Graph
D3FEND is a knowledge base of cybersecurity countermeasure techniques. In the simplest sense, it is a catalog of defensive cybersecurity techniques and their relationships to offensive/adversary techniques. The primary goal of the initial D3FEND release is to help standardize the vocabulary used to
https://d3fend.mitre.org/
MITRE ATT&CK®
https://attack.mitre.org/
The Center for Threat-Informed Defense
An R&D organization focused on advancing the state of the art and the state of the practice in threat-informed defense. - The Center for Threat-Informed Defense
https://github.com/center-for-threat-informed-defense
Analytics
Cyber Analytics Repository
https://car.mitre.org/analytics/
Commits · mitre-attack/car
Cyber Analytics Repository. Contribute to mitre-attack/car development by creating an account on GitHub.
https://github.com/mitre-attack/car/commits/master/
ATT&CK Changes
https://attack.mitre.org/docs/changelogs/v13.1-v14.0/changelog-detailed.html

Living off lands

lolol.farm — Living Off the Living Off the Land
A curated index of Living Off the Land security research projects.
https://lolol.farm/
LOLBAS
https://lolbas-project.github.io/
GTFOBins
GTFOBins is a curated list of Unix-like executables that can be used to bypass local security restrictions in misconfigured systems.
https://gtfobins.github.io/
WTFBins
WTFBins: benign applications that exhibit suspicious behavior
https://wtfbins.wtf/
LOLDrivers
https://www.loldrivers.io/
LOTS Project - Living Off Trusted Sites
https://lots-project.com/
Filesec.io
https://filesec.io/
lolol.farm — Living Off the Living Off the Land
A curated index of Living Off the Land security research projects.
https://lolol.farm/
MalAPI.io
https://malapi.io/
persistence-info.github.io
https://persistence-info.github.io/
Home - Unprotect Project
https://unprotect.it/
WADComs
https://wadcoms.github.io/
HijackLibs.net
HijackLibs provides an curated list of DLL Hijacking opportunities: mappings between DLLs and vulnerable executables, with additional metadata for more context. For defenders, this project can provide valuable information when trying to detect DLL Hijacking attempts; for red teamers, this project ca
https://hijacklibs.net/
LoFP
https://br0k3nlab.com/LoFP/

Triage IPs’, domain’s, hashes

LevelBlue - Open Threat Exchange
Learn about the latest cyber threats. Research, collaborate, and share threat intelligence in real time. Protect yourself and the community against today
https://otx.alienvault.com/
VirusTotal
VirusTotal
https://www.virustotal.com/
Validin
Validin enables threat intelligence teams with comprehensive DNS, host response, registration, certificate, and enrichment.
https://app.validin.com/
URL and website scanner - urlscan.io
urlscan.io - Website scanner for suspicious and malicious URLs
https://urlscan.io/
ThreatFox | Share Indicators Of Compromise (IOCs)
ThreatFox is a project of abuse.ch with the goal of sharing indicators of compromise (IOCs)
https://threatfox.abuse.ch/
URLhaus | Malware URL exchange
URLhaus is a project operated by abuse.ch with the purpose of sharing malicious URLs that are being used for malware distribution
https://urlhaus.abuse.ch/
FOFA Search Engine
FOFA is a Cyberspace search engine. By conducting Cyberspace mapping, it can help researchers or enterprises quickly match network assets, such as vulnerability impact range analysis, application distribution statistics, and application popularity ranking statistics. FOFA is a powerful tool that can
https://en.fofa.info/
CensysGPT Beta
Generate Censys Search Queries
https://gpt.censys.io/

https://search.censys.io/

Shodan
Search engine of Internet-connected devices. Create a free account to get started.
https://www.shodan.io/
LevelBlue - Open Threat Exchange
Learn about the latest cyber threats. Research, collaborate, and share threat intelligence in real time. Protect yourself and the community against today
https://otx.alienvault.com/
crt.sh | Certificate Search
Free CT Log Certificate Search Tool from Sectigo (formerly Comodo CA)
https://crt.sh/
DeHashed — #FreeThePassword
Have you been compromised? DeHashed provides free deep-web scans and protection against credential leaks. A modern personal asset search engine created for security analysts, journalists, security companies, and everyday people to help secure accounts and provide insight on compromised assets. Free
https://www.dehashed.com/
Automated Malware Analysis - Joe Sandbox Cloud Pro
Joe Sandbox Cloud Pro Interface
https://jbxcloud.joesecurity.org/
MX Lookup Tool - Check your DNS MX Records online - MxToolbox
https://mxtoolbox.com/
IBM X-Force Exchange
IBM X-Force Exchange is a threat intelligence sharing platform enabling research on security threats, aggregation of intelligence, and collaboration with peers
https://exchange.xforce.ibmcloud.com/
Whois Lookup, Domain Availability & IP Search - DomainTools
Research domain ownership with Whois Lookup: Get ownership info, IP address history, rank, traffic, SEO & more. Find available domains & domains for sale.
https://whois.domaintools.com/
Uncoder IO | Roota & Sigma Rules Converter | SOC Prime
Free online detection engineering IDE and translation engine for Roota & Sigma rules.
https://uncoder.io/
Check if a Website is Malicious/Scam or Safe/Legit | URLVoid
Free website reputation checker tool lets you scan a website with multiple website reputation/blocklist services to check if the website is safe and legit or malicious. Check the online reputation of a website to better detect potentially malicious and scam websites.
https://www.urlvoid.com/
IP Address Tools, Network Tools, DNS Tools | IPVoid
We offer a vast range of IP address tools to discover details about IP addresses. IP blacklist check, whois lookup, dns lookup, ping, and more!
https://www.ipvoid.com/

https://www.abuseipdb.com/

DNSDumpster - Find & lookup dns records for recon & research
Free domain research tool to discover hosts related to a domain. Find visible hosts from the attackers perspective for Red and Blue Teams.
https://dnsdumpster.com/

https://labs.inquest.net/

https://threatbook.io/ip

https://www.binaryedge.io/

Hunter Search Engine
Internet Search Engines For Security Researchers
https://hunter.how/
GreyNoise Visualizer | GreyNoise Visualizer
At GreyNoise, we collect and analyze untargeted, widespread, and opportunistic scan and attack activity that reaches every server directly connected to the Internet.
https://viz.greynoise.io/trends?view=trending
IPinfo | The Trusted IP Data Provider for Developers & Enterprises
IPinfo delivers fast, accurate, and reliable IP data to power fraud detection, geolocation, analytics, and more. Trusted by over 500,000 developers.
https://ipinfo.io/
DNSDumpster - Find & lookup dns records for recon & research
Free domain research tool to discover hosts related to a domain. Find visible hosts from the attackers perspective for Red and Blue Teams.
https://dnsdumpster.com/

Rules and detection logic

GitHub - SigmaHQ/sigma: Main Sigma Rule Repository
Main Sigma Rule Repository. Contribute to SigmaHQ/sigma development by creating an account on GitHub.
https://github.com/SigmaHQ/sigma
Commits · SigmaHQ/sigma
Main Sigma Rule Repository. Contribute to SigmaHQ/sigma development by creating an account on GitHub.
https://github.com/SigmaHQ/sigma/commits/master
Azure-Sentinel/Solutions at master · Azure/Azure-Sentinel
Cloud-native SIEM for intelligent security analytics for your entire enterprise. - Azure/Azure-Sentinel
https://github.com/Azure/Azure-Sentinel/tree/master/Solutions
GitHub - elastic/detection-rules
Contribute to elastic/detection-rules development by creating an account on GitHub.
https://github.com/elastic/detection-rules
GitHub - redcanaryco/atomic-red-team: Small and highly portable detection tests based on MITRE's ATT&CK.
Small and highly portable detection tests based on MITRE's ATT&CK. - redcanaryco/atomic-red-team
https://github.com/redcanaryco/atomic-red-team
GitHub - rapid7/metasploit-framework: Metasploit Framework
Metasploit Framework. Contribute to rapid7/metasploit-framework development by creating an account on GitHub.
https://github.com/rapid7/metasploit-framework
GitHub - joesecurity/sigma-rules: Sigma rules from Joe Security
Sigma rules from Joe Security. Contribute to joesecurity/sigma-rules development by creating an account on GitHub.
https://github.com/joesecurity/sigma-rules
GitHub - Cisco-Talos/osquery_queries: Cisco Orbital - Osquery queries by Talos
Cisco Orbital - Osquery queries by Talos. Contribute to Cisco-Talos/osquery_queries development by creating an account on GitHub.
https://github.com/Cisco-Talos/osquery_queries
GitHub - InQuest/yara-rules-vt: Collection of YARA rules designed for usage through VirusTotal.com.
Collection of YARA rules designed for usage through VirusTotal.com. - InQuest/yara-rules-vt
https://github.com/InQuest/yara-rules-vt
Splunk Security Content
Welcome to Splunk Security Content See What Is New! - Latest Update: v6.3.0 Download Latest Version 2128 Splunk Detections built to find evil. Detections 363 Analytic Stories to address use cases. Analytic Stories 86 Automated playbook responses. Playbooks What's New Enable your SOC with Proven dete
https://research.splunk.com/
Network
https://research.splunk.com/categories/network
cloud-siem-content-catalog/rules at master · SumoLogic/cloud-siem-content-catalog
Contribute to SumoLogic/cloud-siem-content-catalog development by creating an account on GitHub.
https://github.com/SumoLogic/cloud-siem-content-catalog/blob/master/rules
Prebuilt rule reference | Elastic Security [8.19] | Elastic
https://www.elastic.co/guide/en/security/current/prebuilt-rules.html
Commits · elastic/detection-rules
Contribute to elastic/detection-rules development by creating an account on GitHub.
https://github.com/elastic/detection-rules/commits/main/
Elastic Detection Rules
Detection Rules is the home for rules used by Elastic Security.
https://elastic.github.io/detection-rules-explorer/
Proofpoint Emerging Threats Rules
https://rules.emergingthreats.net/
GitHub - projectdiscovery/nuclei-templates: Community curated list of templates for the nuclei engine to find security vulnerabilities.
Community curated list of templates for the nuclei engine to find security vulnerabilities. - projectdiscovery/nuclei-templates
https://github.com/projectdiscovery/nuclei-templates
Neo23x0 - Overview
#DFIR #Sigma #YARA #Rust #Python #Go . Neo23x0 has 156 repositories available. Follow their code on GitHub.
https://github.com/Neo23x0

IOC lists and THREATs
GitHub - CronUp/Malware-IOCs
Contribute to CronUp/Malware-IOCs development by creating an account on GitHub.
https://github.com/CronUP/Malware-IOCs
GitHub - executemalware/Malware-IOCs
Contribute to executemalware/Malware-IOCs development by creating an account on GitHub.
https://github.com/executemalware/Malware-IOCs
pr0xylife - Overview
pr0xylife has 27 repositories available. Follow their code on GitHub.
https://github.com/pr0xylife
GitHub - Gi7w0rm/MalwareConfigLists: Just some lists of Malware Configs
Just some lists of Malware Configs. Contribute to Gi7w0rm/MalwareConfigLists development by creating an account on GitHub.
https://github.com/Gi7w0rm/MalwareConfigLists
https://isc.sans.edu/api/recentdomains/today?json
GitHub - MISP/misp-warninglists: Warning lists to inform users of MISP about potential false-positives or other information in indicators
Warning lists to inform users of MISP about potential false-positives or other information in indicators - MISP/misp-warninglists
https://github.com/MISP/misp-warninglists
Toxin (@0xToxin) on X
A collection of 333 animated generative artworks, each evolving with infectious color, motion, and form. CA: 0x4C7874d3409a3AF85bdB3D575053292F62307a07
https://twitter.com/0xToxin

Phish

https://www.phishtank.com/phish_archive.php

https://phishstats.info:8443/public/dashboard/3bd497a3-9d59-441a-a4e8-6b7544312257

https://phishstats.info:8443/public/dashboard/096f9d39-441c-44d2-abbd-ea065e31c74a?start=2020-05-01

https://phishstats.info/analytics.html

Other
blackorbird - Overview
APT hunter threat analyst . blackorbird has 46 repositories available. Follow their code on GitHub.
https://github.com/blackorbird
Datacadamia - data all the way
Computer science from a data perspective
https://datacadamia.com/start
ORKL
ORKL Threat Intelligence Library
https://orkl.eu/
ThreatMiner.org | Data Mining for Threat Intelligence
ThreatMiner is a threat intelligence portal that provides information on indicators of compromise (IOC) such as domains, IP address, malware samples (MD5, SHA1 and SHA256), SSL certificates, WHOIS information and malicious URLs such as phishing and malware links.
https://www.threatminer.org/index.php
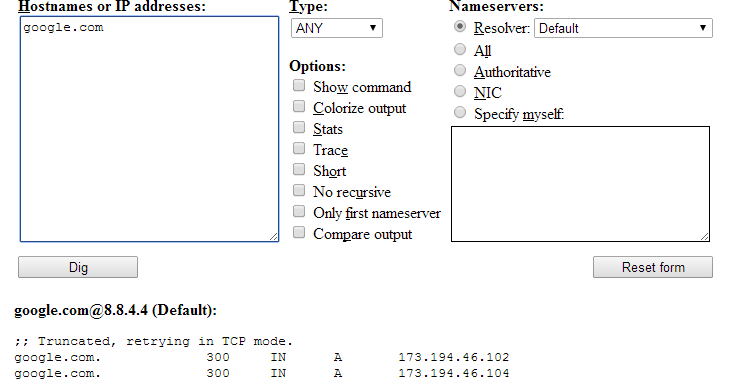
DigWebInterface.com
Extensive web interface to dig
https://digwebinterface.com/
PageXray by FouAnalytics
https://pagexray.fouanalytics.com/
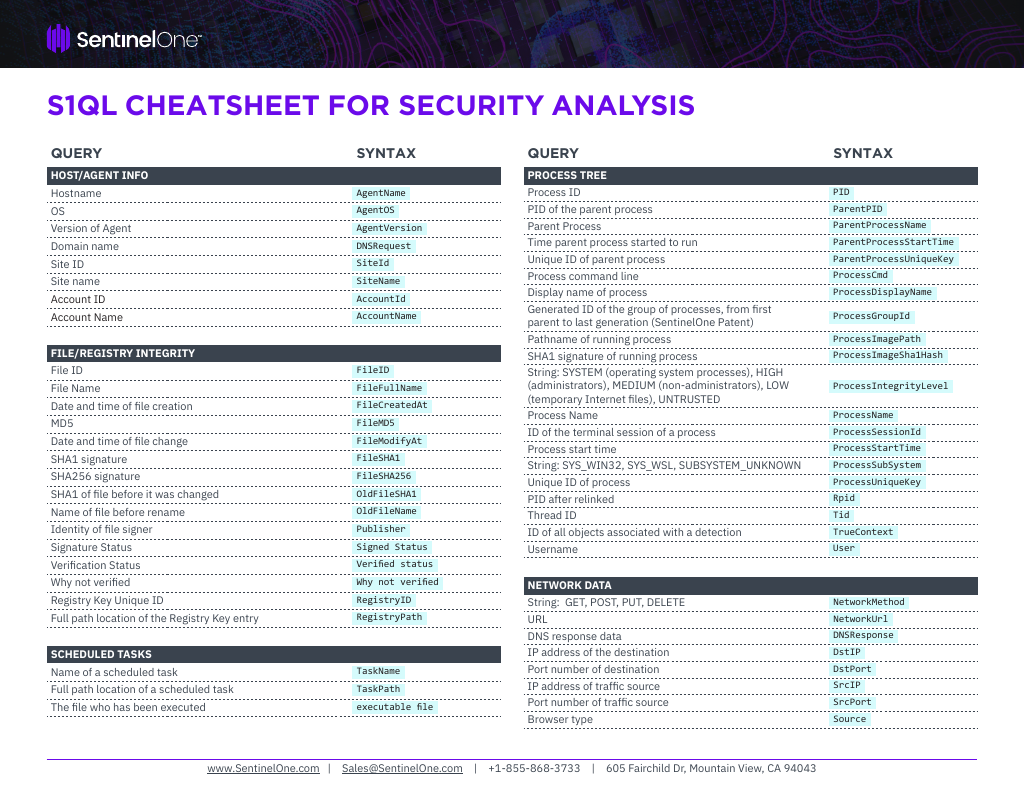
SentinelOne Deep Visibility CheatSheet (Landscape)
Everything a Security Analyst Needs to Know
https://assets.sentinelone.com/dv/sentinel-one-dv-chea-1?xs=105462#page=1
Programs
Some programs I developed and share: List the Security Descriptor of Shares UserAssist Utility Binary Tools OllyStepNSearch USBVirusScan EICARgen XORSearch FileGen ZIPEncryptFTP ExtractScripts Tran…
https://blog.didierstevens.com/programs/
Sysinternals - Sysinternals
Library, learning resources, downloads, support, and community. Evaluate and find out how to install, deploy, and maintain Windows with Sysinternals utilities.
https://learn.microsoft.com/en-us/sysinternals/

https://httpstat.us/

ReqRes | Free REST API for developers
Free REST API for testing and prototyping with real responses, no signup needed. Or build your own backend with collections, auth, and logs at app.reqres.in.
https://reqres.in/

https://www.lockheedmartin.com/content/dam/lockheed-martin/rms/documents/cyber/LM-White-Paper-Intel-Driven-Defense.pdf

https://www.activeresponse.org/wp-content/uploads/2013/07/diamond.pdf

https://update.avlab.co/

https://cristi075.github.io/ ex of writeups

https://www.ransomlook.io/recent ex of threat list

https://gitlab.com/exploit-database/exploitdb ExploitDB updates

https://docs.velociraptor.app/exchange/ velociraptor updates

https://medium.com/tag/cybersecurity cybersecurity articles

CVE
Activity Feed | AttackerKB
Not all vulns are created equal.
https://attackerkb.com/activity-feed
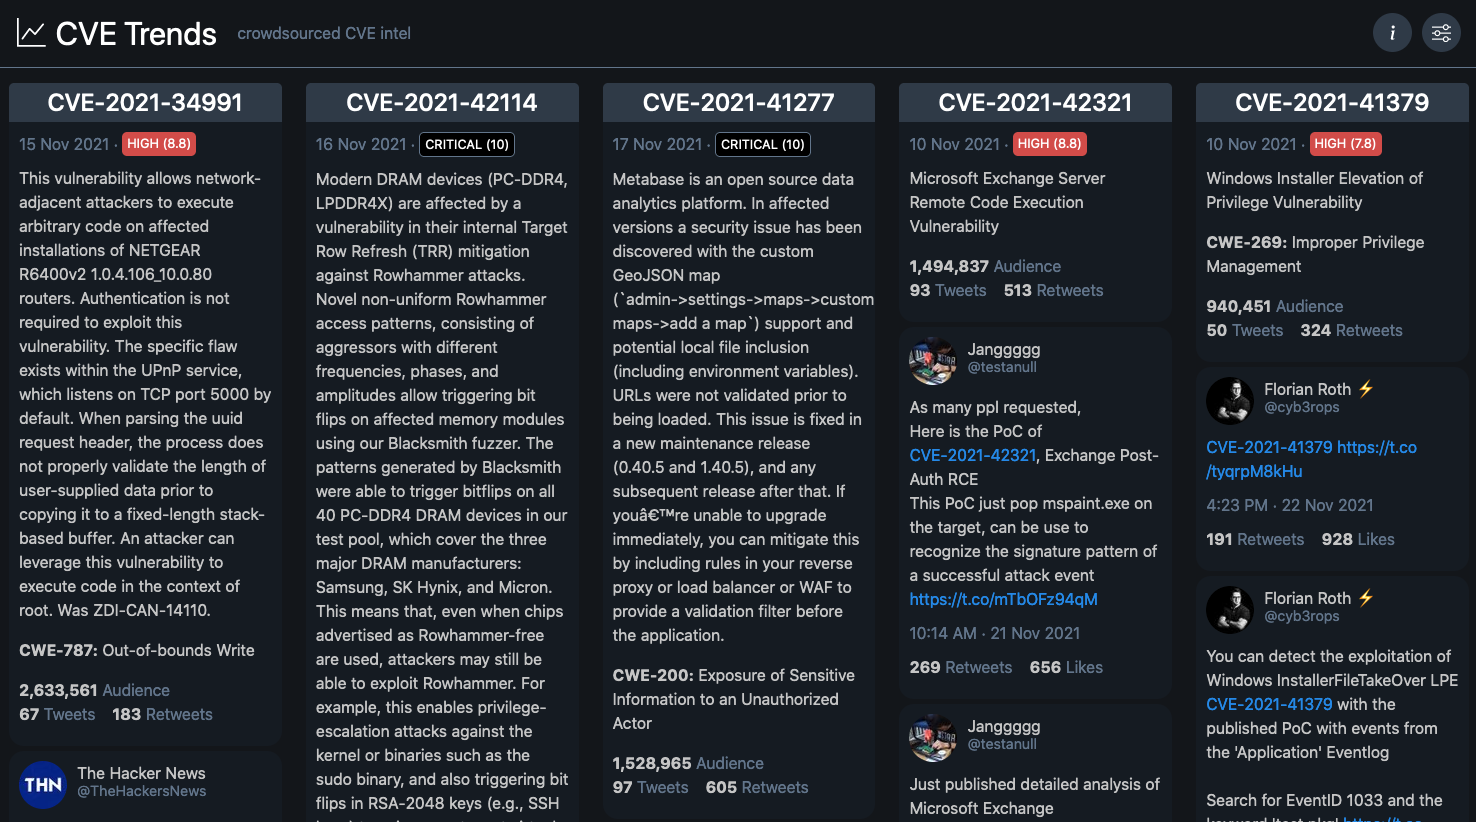
CVE Trends - crowdsourced CVE intel
Monitor trending CVEs in real-time; crowdsourced intel sourced from Twitter, NIST NVD, Reddit, and GitHub.
https://cvetrends.com/

Microsoft

Security Update Guide - Microsoft Security Response Center
https://msrc.microsoft.com/update-guide/releaseNote
Security Update Guide - Microsoft Security Response Center
https://msrc.microsoft.com/update-guide/vulnerability
Sign in to your account
https://ti.defender.microsoft.com/
Blog MSRC | Microsoft Security Response Center
Microsoft Security Response Center Blog
https://msrc.microsoft.com/blog/2023/
Security Update Guide - Microsoft Security Response Center
https://msrc.microsoft.com/update-guide/

Tools
de4js
JavaScript Deobfuscator and Unpacker
https://lelinhtinh.github.io/de4js/
SCYTHE
SCYTHE has 2 repositories available. Follow their code on GitHub.
https://github.com/scythe-io
GitHub - opencybersecurityalliance/kestrel-lang: Kestrel threat hunting language: building reusable, composable, and shareable huntflows acr
Kestrel threat hunting language: building reusable, composable, and shareable huntflows across different data sources and threat intel. - opencybersecurityalliance/kestrel-lang
https://github.com/opencybersecurityalliance/kestrel-lang
Free Online VBScript/VBS Obfuscator/deobfuscator, Protect Your VBScript, VBS Encrytpion
This online utility allows you to obfuscate your VBScript so that your VBScript can be protected (encrypted) if you do not want others to read your VBS source code
https://isvbscriptdead.com/vbs-obfuscator/
GitHub - swisskyrepo/PayloadsAllTheThings: A list of useful payloads and bypass for Web Application Security and Pentest/CTF
A list of useful payloads and bypass for Web Application Security and Pentest/CTF - swisskyrepo/PayloadsAllTheThings
https://github.com/swisskyrepo/PayloadsAllTheThings/tree/master
awesome-lists/Lists at main · mthcht/awesome-lists
Awesome Security lists for SOC/CERT/CTI. Contribute to mthcht/awesome-lists development by creating an account on GitHub.
https://github.com/mthcht/awesome-lists/tree/main/Lists
Red Team
HackTricks - HackTricks
HackTricks is a cybersecurity knowledge base with practical pentesting, red team, web, cloud, binary exploitation, and privilege escalation techniques.
https://book.hacktricks.xyz/
Blog - Trickest
Notes from the team building Trickest: offensive-security workflows, discovery at scale, and what we learn running it in production.
https://trickest.com/blog/
GitHub - coreb1t/awesome-pentest-cheat-sheets: Collection of the cheat sheets useful for pentesting
Collection of the cheat sheets useful for pentesting - coreb1t/awesome-pentest-cheat-sheets
https://github.com/coreb1t/awesome-pentest-cheat-sheets
GitHub - Crypto-Cat/CTF: CTF challenge (mostly pwn) files, scripts etc
CTF challenge (mostly pwn) files, scripts etc. Contribute to Crypto-Cat/CTF development by creating an account on GitHub.
https://github.com/Crypto-Cat/CTF
GitHub - WesleyWong420/OPSEC-Tradecraft: Collection of OPSEC Tradecraft and TTPs for Red Team Operations
Collection of OPSEC Tradecraft and TTPs for Red Team Operations - WesleyWong420/OPSEC-Tradecraft
https://github.com/WesleyWong420/OPSEC-Tradecraft
What is ired.team notes? | Red Team Notes
These are notes about all things focusing on, but not limited to, red teaming and offensive security.
https://ired.team/
ARTToolkit
https://arttoolkit.github.io/
GitHub - aliasrobotics/cai: Cybersecurity AI (CAI), the framework for AI Security
Cybersecurity AI (CAI), the framework for AI Security - aliasrobotics/cai
https://github.com/aliasrobotics/cai?tab=readme-ov-file
Blue team
GitHub - ovh/debian-cis: PCI-DSS compliant Debian 11/12/13 hardening
PCI-DSS compliant Debian 11/12/13 hardening. Contribute to ovh/debian-cis development by creating an account on GitHub.
https://github.com/ovh/debian-cis
GitHub - hardenedlinux/harbian-audit: Hardened Debian GNU/Linux distro auditing
Hardened Debian GNU/Linux distro auditing. Contribute to hardenedlinux/harbian-audit development by creating an account on GitHub.
https://github.com/hardenedlinux/harbian-audit
https://github.com/HuntDownProject/HEDnsExtractor

Threat
ThreatHunting Home
https://www.threathunting.net/
Sqrrl Archive
https://www.threathunting.net/sqrrl-archive
Threat Intelligence Services for SOC & MSSP - ANY.RUN
Boost triage & response with actionable threat intelligence: TI Lookup for fast indicator context, TI Feeds for verified IOCs, powered by attack data from 15K SOCs.
https://intelligence.any.run/
Home - Unprotect Project
https://unprotect.it/
Insider Threat Matrix™ | Unified Framework For Investigators
ITM™ is an open framework for digital investigators and the cyber security community, to better address the challenges of computer-enabled insider threats.
https://insiderthreatmatrix.org/

Detection

AttackRuleMap
Mapping of Atomic Red Team attack simulations to open-source detection rules (Sigma & Splunk ESCU).
https://attackrulemap.netlify.app/

https://eventlog-compendium.streamlit.app/Audit_Policy_To_Event_ID_Mapping

Hunting

https://www.splunk.com/en_us/pdfs/gated/ebooks/splunk-peak-threat-hunting-framework.pdf
Playbooks
Name SOAR App D3FEND Use Case Risk Notable Block Indicators Attribute Lookup Dispatch Enrichment Cisco Umbrella DNS Denylisting Cisco Umbrella D3-DNSDL Phishing Endpoint Risk Notable Protect Assets and Users AD LDAP Account Locking AD LDAP D3-AL Phishing Endpoint CrowdStrike OAuth API File Eviction
https://research.splunk.com/playbooks/